Check Link Hook
This example demonstrates how to process outgoing NHRP traffic in a scenario using one Tunnel with GRE encapsulation.
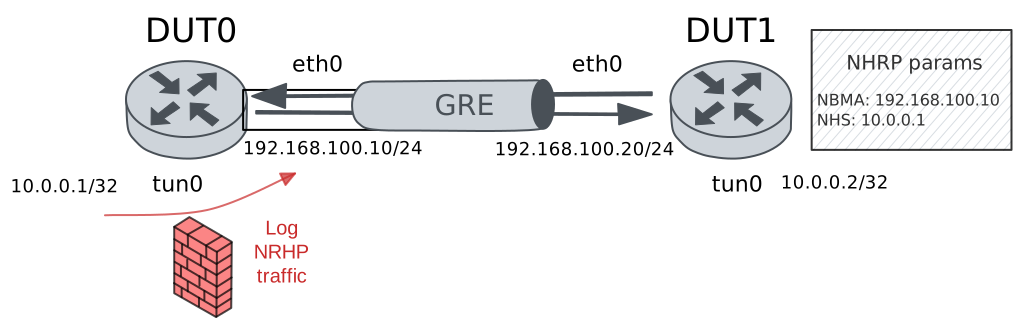
Test Marks In NHRP Traffic
Description
In this scenario, a traffic policy was configured
to log outgoing NHRP traffic, which is non-IP Layer
3 protocol. The special hook link-out can be
used to process these outgoing frames.
Scenario
Step 1: Set the following configuration in DUT0 :
set interfaces ethernet eth0 address 192.168.100.10/24
set interfaces tunnel tun0 address 10.0.0.1/32
set interfaces tunnel tun0 encapsulation gre
set interfaces tunnel tun0 local-address 192.168.100.10
set interfaces tunnel tun0 nhrp
set interfaces tunnel tun0 traffic policy link-in LOG_NHRP
set interfaces tunnel tun0 traffic policy link-out LOG_NHRP
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set traffic policy LOG_NHRP rule 1 log prefix NHRP__
set traffic policy LOG_NHRP rule 1 selector NHRP_SEL
set traffic selector NHRP_SEL rule 1 ether-type 8193
Note
NHRP packets use ethertype 8193 (0x2001).
Step 2: Set the following configuration in DUT1 :
set interfaces ethernet eth0 address 192.168.100.20/24
set interfaces tunnel tun0 address 10.0.0.2/32
set interfaces tunnel tun0 encapsulation gre
set interfaces tunnel tun0 local-address 192.168.100.20
set interfaces tunnel tun0 nhrp holdtime 5
set interfaces tunnel tun0 nhrp nhs 10.0.0.1 nbma 192.168.100.10
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
Step 3: Run the command protocols ip show nhrp on DUT0 and check whether the output matches the following regular expressions:
tun0\s+dynamic\s+10\.0\.0\.2Show output
Iface      Type     Protocol         NBMA             Claimed NBMA     Expires(s)   Flags  Identity
tun0       local    10.0.0.1         192.168.100.10   192.168.100.10   -                   -
tun0       dynamic  10.0.0.2         192.168.100.20   192.168.100.20   4             T
Step 4: Run the command system journal show | cat on DUT0 and check whether the output matches the following regular expressions:
\[NHRP__-1\] ACCEPT IN=tun0 OUT=\w+
\[NHRP__-1\] ACCEPT IN= OUT=tun0
Show output
Sep 16 13:57:39.000266 osdx systemd-timedated[36715]: Changed local time to Wed 2026-09-16 13:57:39 UTC
Sep 16 13:57:39.001377 osdx systemd-journald[2259]: Time jumped backwards, rotating.
Sep 16 13:57:39.001833 osdx OSDxCLI[5354]: User 'admin' executed a new command: 'set date 2026-09-16 13:57:39'.
Sep 16 13:57:39.333995 osdx systemd-journald[2259]: Runtime Journal (/run/log/journal/9a65ea3d62e846a9833effd22444e4c4) is 1.9M, max 13.8M, 11.9M free.
Sep 16 13:57:39.337371 osdx systemd-journald[2259]: Received client request to rotate journal, rotating.
Sep 16 13:57:39.337427 osdx systemd-journald[2259]: Vacuuming done, freed 0B of archived journals from /run/log/journal/9a65ea3d62e846a9833effd22444e4c4.
Sep 16 13:57:39.344247 osdx OSDxCLI[5354]: User 'admin' executed a new command: 'system journal clear'.
Sep 16 13:57:39.592038 osdx OSDxCLI[5354]: User 'admin' executed a new command: 'system coredump delete all'.
Sep 16 13:57:39.856333 osdx OSDxCLI[5354]: User 'admin' entered the configuration menu.
Sep 16 13:57:39.940884 osdx OSDxCLI[5354]: User 'admin' added a new cfg line: 'set interfaces ethernet eth0 address 192.168.100.10/24'.
Sep 16 13:57:40.036530 osdx OSDxCLI[5354]: User 'admin' added a new cfg line: 'set interfaces tunnel tun0 traffic policy link-out LOG_NHRP'.
Sep 16 13:57:40.097906 osdx OSDxCLI[5354]: User 'admin' added a new cfg line: 'set interfaces tunnel tun0 traffic policy link-in LOG_NHRP'.
Sep 16 13:57:40.194811 osdx OSDxCLI[5354]: User 'admin' added a new cfg line: 'set interfaces tunnel tun0 address 10.0.0.1/32'.
Sep 16 13:57:40.265078 osdx OSDxCLI[5354]: User 'admin' added a new cfg line: 'set interfaces tunnel tun0 encapsulation gre'.
Sep 16 13:57:40.368711 osdx OSDxCLI[5354]: User 'admin' added a new cfg line: 'set interfaces tunnel tun0 local-address 192.168.100.10'.
Sep 16 13:57:40.462226 osdx OSDxCLI[5354]: User 'admin' added a new cfg line: 'set interfaces tunnel tun0 nhrp'.
Sep 16 13:57:40.563378 osdx OSDxCLI[5354]: User 'admin' added a new cfg line: 'set traffic policy LOG_NHRP rule 1 log prefix NHRP__'.
Sep 16 13:57:40.680639 osdx OSDxCLI[5354]: User 'admin' added a new cfg line: 'set traffic policy LOG_NHRP rule 1 selector NHRP_SEL'.
Sep 16 13:57:40.799003 osdx OSDxCLI[5354]: User 'admin' added a new cfg line: 'set traffic selector NHRP_SEL rule 1 ether-type 8193'.
Sep 16 13:57:40.874106 osdx OSDxCLI[5354]: User 'admin' added a new cfg line: 'show working'.
Sep 16 13:57:40.985761 osdx ubnt-cfgd[36752]: inactive
Sep 16 13:57:41.081735 osdx systemd[1]: Reloading frr.service - FRRouting...
Sep 16 13:57:41.099377 osdx watchfrr[36556]: [NG1AJ-FP2TQ] Terminating on signal
Sep 16 13:57:41.200523 osdx frrinit.sh[36787]: Stopped watchfrr.
Sep 16 13:57:41.201783 osdx frrinit.sh[36787]: Starting watchfrr with command: '  /usr/lib/frr/watchfrr  -d  --min-restart-interval 1 --max-restart-interval 600 --timeout 600 --restart-timeout 600 mgmtd zebra nhrpd staticd'.
Sep 16 13:57:41.211566 osdx watchfrr[36805]: [T83RR-8SM5G] watchfrr 10.6.0 starting: vty@0
Sep 16 13:57:41.211629 osdx watchfrr[36805]: [QDG3Y-BY5TN] mgmtd state -> up : connect succeeded
Sep 16 13:57:41.211656 osdx watchfrr[36805]: [QDG3Y-BY5TN] zebra state -> up : connect succeeded
Sep 16 13:57:41.211693 osdx watchfrr[36805]: [ZCJ3S-SPH5S] nhrpd state -> down : initial connection attempt failed
Sep 16 13:57:41.211696 osdx watchfrr[36805]: [QDG3Y-BY5TN] staticd state -> up : connect succeeded
Sep 16 13:57:41.211863 osdx watchfrr[36805]: [YFT0P-5Q5YX] Forked background command [pid 36806]: /usr/lib/frr/watchfrr.sh restart nhrpd
Sep 16 13:57:41.216644 osdx frrinit.sh[36806]: Cannot stop nhrpd: pid file not found
Sep 16 13:57:41.217917 osdx watchfrr.sh[36811]: Cannot stop nhrpd: pid file not found
Sep 16 13:57:41.233608 osdx zebra[1832]: [V98V0-MTWPF] client 41 says hello and bids fair to announce only nhrp routes vrf=0
Sep 16 13:57:41.242904 osdx frrinit.sh[36816]: sh: line 1: ipsec: command not found
Sep 16 13:57:41.257754 osdx nhrpd[36813]: [W9E3X-A5P3X] nhrpd: set-config-loaded received, marking as loaded
Sep 16 13:57:41.259485 osdx watchfrr[36805]: [QDG3Y-BY5TN] nhrpd state -> up : connect succeeded
Sep 16 13:57:41.259492 osdx watchfrr[36805]: [KWE5Q-QNGFC] all daemons up, doing startup-complete notify
Sep 16 13:57:41.260754 osdx frrinit.sh[36787]: Started watchfrr.
Sep 16 13:57:41.400862 osdx systemd[1]: Reloaded frr.service - FRRouting.
Sep 16 13:57:41.441375 osdx kernel: 8021q: adding VLAN 0 to HW filter on device eth0
Sep 16 13:57:41.490409 osdx WARNING[36912]: No supported link modes on interface eth0
Sep 16 13:57:41.492265 osdx modulelauncher[36912]: osdx.utils.xos cmd error: /sbin/ethtool -A eth0 autoneg on
Sep 16 13:57:41.492277 osdx modulelauncher[36912]: Command '/sbin/ethtool -A eth0 autoneg on' returned non-zero exit status 76.
Sep 16 13:57:41.493899 osdx modulelauncher[36912]: osdx.utils.xos cmd error: /sbin/ethtool -s eth0 autoneg on advertise Pause off Asym_Pause off --
Sep 16 13:57:41.493909 osdx modulelauncher[36912]: Command '/sbin/ethtool -s eth0 autoneg on advertise Pause off Asym_Pause off --' returned non-zero exit status 75.
Sep 16 13:57:41.511577 osdx (udev-worker)[36929]: Network interface NamePolicy= disabled on kernel command line.
Sep 16 13:57:41.995294 osdx cfgd[1892]: [5354]Completed change to active configuration
Sep 16 13:57:41.995911 osdx OSDxCLI[5354]: User 'admin' committed the configuration.
Sep 16 13:57:42.024857 osdx OSDxCLI[5354]: User 'admin' left the configuration menu.
Sep 16 13:57:43.815671 osdx OSDxCLI[5354]: User 'admin' executed a new command: 'protocols ip show nhrp'.
Sep 16 13:57:44.501376 osdx kernel: [NHRP__-1] ACCEPT IN=tun0 OUT= MAC=45:00:00:74:bd:3d:40:00:40:2f:33:ae:c0:a8:64:14:c0:a8:64:0a:00:00:20:01
Sep 16 13:57:44.501445 osdx kernel: [NHRP__-1] ACCEPT IN= OUT=tun0 MAC=45:01:00:00:00:00:40:00:40:2f:00:00:c0:a8:64:0a:c0:a8:64:14:00:00:20:01
Sep 16 13:57:44.501454 osdx kernel: [NHRP__-1] ACCEPT IN=tun0 OUT=eth0 MAC=00:01:08:00:00:00:00:00:00:40:00:70:2b:43:00:34:01:04:04:00:04:04:00:02
Sep 16 13:57:45.499302 osdx kernel: [NHRP__-1] ACCEPT IN=tun0 OUT= MAC=45:00:00:74:bd:80:40:00:40:2f:33:6b:c0:a8:64:14:c0:a8:64:0a:00:00:20:01
Sep 16 13:57:45.499391 osdx kernel: [NHRP__-1] ACCEPT IN= OUT=tun0 MAC=45:01:00:00:00:00:40:00:40:2f:00:00:c0:a8:64:0a:c0:a8:64:14:00:00:20:01
Sep 16 13:57:45.499405 osdx kernel: [NHRP__-1] ACCEPT IN=tun0 OUT=eth0 MAC=00:01:08:00:00:00:00:00:00:40:00:70:2b:42:00:34:01:04:04:00:04:04:00:02
Sep 16 13:57:45.922381 osdx OSDxCLI[5354]: User 'admin' executed a new command: 'protocols ip show nhrp'.
Step 5: Run the command traffic policy show on DUT0 and check whether the output matches the following regular expressions:
1\s+NHRP_SEL\s+\b[^0]\d*Show output
Policy LOG_NHRP -- ifc tun0 -- hook link-in prio very-high

---------------------------------------------------------------
rule   selector  pkts match  pkts eval  bytes match  bytes eval
---------------------------------------------------------------
1      NHRP_SEL           4          4          456         456
---------------------------------------------------------------
Total                     4          4          456         456

Policy LOG_NHRP -- ifc tun0 -- hook link-out prio very-high

---------------------------------------------------------------
rule   selector  pkts match  pkts eval  bytes match  bytes eval
---------------------------------------------------------------
1      NHRP_SEL           2          2          272         272
---------------------------------------------------------------
Total                     2          2          272         272