Netflow
These scenarios demonstrate how to configure and use NetFlow to collect and export local TCP flows, covering different modes and configuration options.
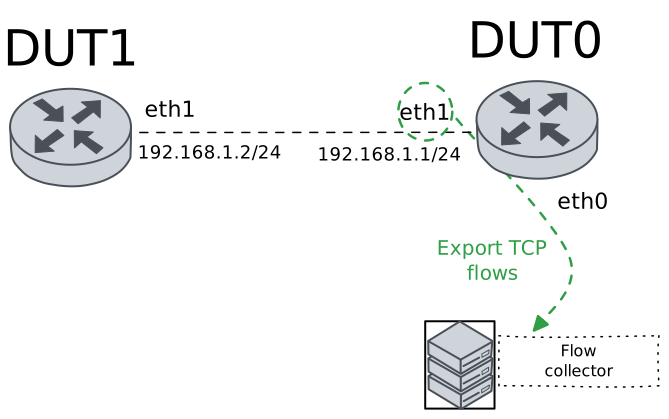
Test NetFlow Scenario
Description
These examples demonstrate how to configure and use NetFlow to collect and export locally generated TCP flows across different configuration modes.
Scenario
Example 1
Step 1: Set the following configuration in DUT0 :
set interfaces ethernet eth0 address 10.215.168.64/24
set interfaces ethernet eth1 address 192.168.1.1/24
set interfaces ethernet eth1 flow egress selector TCP_SEL
set interfaces ethernet eth1 flow ingress selector TCP_SEL
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set system netflow destination 10.215.168.1
set system netflow engine-id 1111
set traffic selector TCP_SEL rule 1 protocol tcp
Step 2: Set the following configuration in DUT1 :
set interfaces ethernet eth1 address 192.168.1.2/24
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
Step 3: Run the command system netflow show status on DUT0 and check whether the output matches the following regular expressions:
Protocol\sversion\s10\s\(ipfix\)
Export:.*Errors 0 pkts
sock0:\s127.0.0.1:2055,.*err: sndbuf reached 0, connect 0, cberr \d+, other 0
Show output
ipt_NETFLOW 2.6, srcversion 78C6C2B77E78F740D6A6F59; dir
Protocol version 10 (ipfix), refresh-rate 20, timeout-rate 30, (templates 0, active 1).
Timeouts: active 1800s, inactive 15s. Maxflows 2000000
Flows: active 0 (peak 2 reached 0d0h1m ago), mem 491K, worker delay 25/250 [1..25] (36 ms, 0 us, 0:0 [cpu1]).
Hash: size 62967 (mem 491K), metric 1.00 [1.00, 1.00, 1.00]. InHash: 0 pkt, 0 K, InPDU 0, 0.
Rate: 0 bits/sec, 0 packets/sec; Avg 1 min: 801 bps, 0 pps; 5 min: 389 bps, 0 pps
cpu#     pps; <search found new [metric], trunc frag alloc maxflows>, traffic: <pkt, bytes>, drop: <pkt, bytes>
Total      0;      0    114     16 [1.00],    0    0    0    0, traffic: 165, 0 MB, drop: 0, 0 K
cpu0       0;      0     24      8 [1.00],    0    0    0    0, traffic: 66, 0 MB, drop: 0, 0 K
cpu1       0;      0     84      8 [1.00],    0    0    0    0, traffic: 65, 0 MB, drop: 0, 0 K
cpu2       0;      0      2      0 [1.00],    0    0    0    0, traffic: 14, 0 MB, drop: 0, 0 K
cpu3       0;      0      4      0 [1.00],    0    0    0    0, traffic: 20, 0 MB, drop: 0, 0 K
Export: Rate 0 bytes/s; Total 26 pkts, 0 MB, 16 flows; Errors 0 pkts; Traffic lost 0 pkts, 0 Kbytes, 0 flows.
sock0: 127.0.0.1:2055, sndbuf 212992, filled 1, peak 1; err: sndbuf reached 0, connect 0, cberr 0, other 0
Step 4: Ping the IP address 192.168.1.2 from DUT0:
admin@DUT0$ ping 192.168.1.2 count 1 size 56 timeout 1Show output
PING 192.168.1.2 (192.168.1.2) 56(84) bytes of data.
64 bytes from 192.168.1.2: icmp_seq=1 ttl=64 time=0.405 ms

--- 192.168.1.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.405/0.405/0.405/0.000 ms
Step 5: Ping the IP address 10.215.168.1 from DUT0:
admin@DUT0$ ping 10.215.168.1 count 1 size 56 timeout 1Show output
PING 10.215.168.1 (10.215.168.1) 56(84) bytes of data.
64 bytes from 10.215.168.1: icmp_seq=1 ttl=64 time=0.174 ms

--- 10.215.168.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.174/0.174/0.174/0.000 ms
Step 6: Initiate a tcp connection from DUT1 to DUT0 and exchange messages between both endpoints
admin@DUT0$ monitor test connection server 8080 tcp
admin@DUT1$ monitor test connection client 192.168.1.1 8080 tcp
Step 7: Run the command system netflow show flows detailed on DUT0 and check whether the output matches the following regular expressions:
3\s+0\s+192.168.1.2:\d+\s+192.168.1.1:8080\s+6(\s+\S+){7}\s+[1-9]\d*
0\s+3\s+192.168.1.1:8080\s+192.168.1.2:\d+\s+6(\s+\S+){7}\s+[1-9]\d*
Show output
------------------------------------------------------------------------------------------
Field       Description
------------------------------------------------------------------------------------------
#           Numeric flow identifier
hash        Hash of the flow
a           Shows if the flow is pending of being exported
iif         Input interface
oif         Output interface
src:port    Source IP:PORT
dst:port    Destination IP:PORT
protocol    Protocol identifier
nexthop     Next-hop
mark        Connmark
appid       AppIDs, as 'engine:selector' pairs
tos         Type of service identificator
tcpflags    TCP flags
options     Optional IP options
tcpoptions  TCP Options (MSS, Window Scaling, Selective Acknowledgements, Timestamps, Nop)
pkts        Packets counter
bytes       Bytes counter
ts_first    Timestamp of fist packet that passed through the flow
ts_last     Timestamp of last packet that passed through the flow


--------------------------------------------------------------------------------------------------------------------------------------------------------------
#  hash  a  iif  oif  src:port           dst:port           protocol  nexthop  mark  appid  tos  tcpflags  options  tcpoptions  pkts  bytes  ts_first  ts_last
--------------------------------------------------------------------------------------------------------------------------------------------------------------
1  d055  0  0    3    192.168.1.1:8080   192.168.1.2:56046  6         0.0.0.0  0     -      0x0  0x1b      0x0      0xf1000000  10    628    410       33
2  98da  0  3    0    192.168.1.2:56046  192.168.1.1:8080   6         0.0.0.0  0     -      0x0  0x1b      0x0      0xf1000000  14    836    410       33
Step 8: Run the command system netflow show stats on DUT0 and check whether the output matches the following regular expressions:
eth1\s+egress\s+[1-9]\d*
eth1\s+ingress\s+[1-9]\d*
Show output
--------------------------------------------------------------
iface   mode    pkts match  pkts eval  bytes match  bytes eval
--------------------------------------------------------------
eth1   egress           10         17          628        1368
eth1   ingress          14         15          836         920
--------------------------------------------------------------
Total                   24         32         1464        2288
Example 2
Step 1: Set the following configuration in DUT0 :
set interfaces ethernet eth0 address 10.215.168.64/24
set interfaces ethernet eth1 address 192.168.1.1/24
set interfaces ethernet eth1 flow egress selector TCP_SEL
set interfaces ethernet eth1 flow ingress selector TCP_SEL
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set system netflow destination 10.215.168.1 dtls
set system netflow engine-id 1111
set traffic selector TCP_SEL rule 1 protocol tcp
Step 2: Set the following configuration in DUT1 :
set interfaces ethernet eth1 address 192.168.1.2/24
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
Step 3: Run the command system netflow show status on DUT0 and check whether the output matches the following regular expressions:
Protocol\sversion\s10\s\(ipfix\)
Export:.*Errors 0 pkts
sock0:\s127.0.0.1:2055,.*err: sndbuf reached 0, connect 0, cberr \d+, other 0
Show output
ipt_NETFLOW 2.6, srcversion 78C6C2B77E78F740D6A6F59; dir
Protocol version 10 (ipfix), refresh-rate 20, timeout-rate 30, (templates 0, active 1).
Timeouts: active 1800s, inactive 15s. Maxflows 2000000
Flows: active 0 (peak 2 reached 0d0h1m ago), mem 491K, worker delay 25/250 [1..25] (100 ms, 0 us, 0:0 [cpu2]).
Hash: size 62967 (mem 491K), metric 1.00 [1.00, 1.00, 1.00]. InHash: 0 pkt, 0 K, InPDU 0, 0.
Rate: 0 bits/sec, 0 packets/sec; Avg 1 min: 855 bps, 0 pps; 5 min: 431 bps, 0 pps
cpu#     pps; <search found new [metric], trunc frag alloc maxflows>, traffic: <pkt, bytes>, drop: <pkt, bytes>
Total      0;      0    136     18 [1.00],    0    0    0    0, traffic: 189, 0 MB, drop: 0, 0 K
cpu0       0;      0     24      8 [1.00],    0    0    0    0, traffic: 66, 0 MB, drop: 0, 0 K
cpu1       0;      0     99     10 [1.00],    0    0    0    0, traffic: 82, 0 MB, drop: 0, 0 K
cpu2       0;      0      3      0 [1.00],    0    0    0    0, traffic: 15, 0 MB, drop: 0, 0 K
cpu3       0;      0     10      0 [1.00],    0    0    0    0, traffic: 26, 0 MB, drop: 0, 0 K
Export: Rate 136 bytes/s; Total 29 pkts, 0 MB, 18 flows; Errors 0 pkts; Traffic lost 0 pkts, 0 Kbytes, 0 flows.
sock0: 127.0.0.1:2055, sndbuf 212992, filled 1, peak 1; err: sndbuf reached 0, connect 0, cberr 1, other 0
Step 4: Ping the IP address 192.168.1.2 from DUT0:
admin@DUT0$ ping 192.168.1.2 count 1 size 56 timeout 1Show output
PING 192.168.1.2 (192.168.1.2) 56(84) bytes of data.
64 bytes from 192.168.1.2: icmp_seq=1 ttl=64 time=0.408 ms

--- 192.168.1.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.408/0.408/0.408/0.000 ms
Step 5: Ping the IP address 10.215.168.1 from DUT0:
admin@DUT0$ ping 10.215.168.1 count 1 size 56 timeout 1Show output
PING 10.215.168.1 (10.215.168.1) 56(84) bytes of data.
64 bytes from 10.215.168.1: icmp_seq=1 ttl=64 time=0.426 ms

--- 10.215.168.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.426/0.426/0.426/0.000 ms
Step 6: Initiate a tcp connection from DUT1 to DUT0 and exchange messages between both endpoints
admin@DUT0$ monitor test connection server 8080 tcp
admin@DUT1$ monitor test connection client 192.168.1.1 8080 tcp
Step 7: Run the command system netflow show flows detailed on DUT0 and check whether the output matches the following regular expressions:
3\s+0\s+192.168.1.2:\d+\s+192.168.1.1:8080\s+6(\s+\S+){7}\s+[1-9]\d*
0\s+3\s+192.168.1.1:8080\s+192.168.1.2:\d+\s+6(\s+\S+){7}\s+[1-9]\d*
Show output
------------------------------------------------------------------------------------------
Field       Description
------------------------------------------------------------------------------------------
#           Numeric flow identifier
hash        Hash of the flow
a           Shows if the flow is pending of being exported
iif         Input interface
oif         Output interface
src:port    Source IP:PORT
dst:port    Destination IP:PORT
protocol    Protocol identifier
nexthop     Next-hop
mark        Connmark
appid       AppIDs, as 'engine:selector' pairs
tos         Type of service identificator
tcpflags    TCP flags
options     Optional IP options
tcpoptions  TCP Options (MSS, Window Scaling, Selective Acknowledgements, Timestamps, Nop)
pkts        Packets counter
bytes       Bytes counter
ts_first    Timestamp of fist packet that passed through the flow
ts_last     Timestamp of last packet that passed through the flow


--------------------------------------------------------------------------------------------------------------------------------------------------------------
#  hash  a  iif  oif  src:port           dst:port           protocol  nexthop  mark  appid  tos  tcpflags  options  tcpoptions  pkts  bytes  ts_first  ts_last
--------------------------------------------------------------------------------------------------------------------------------------------------------------
1  49d8  0  0    3    192.168.1.1:8080   192.168.1.2:36368  6         0.0.0.0  0     -      0x0  0x1b      0x0      0xf1000000  9     576    376       30
2  52f8  0  3    0    192.168.1.2:36368  192.168.1.1:8080   6         0.0.0.0  0     -      0x0  0x1b      0x0      0xf1000000  10    628    376       30
Step 8: Run the command system conntrack show on DUT0 and check whether the output matches the following regular expressions:
dst=10.215.168.1.*dport=4740.*packets=[1-9]\d*Show output
udp      17 29 src=10.215.168.64 dst=10.215.168.1 sport=53804 dport=4740 packets=1 bytes=340 [UNREPLIED] src=10.215.168.1 dst=10.215.168.64 sport=4740 dport=53804 packets=0 bytes=0 mark=0 use=1
udp      17 29 src=127.0.0.1 dst=127.0.0.1 sport=45280 dport=2055 packets=1 bytes=236 [UNREPLIED] src=127.0.0.1 dst=127.0.0.1 sport=2055 dport=45280 packets=0 bytes=0 mark=0 use=1
conntrack v1.4.7 (conntrack-tools): 2 flow entries have been shown.
Step 9: Run the command system netflow show stats on DUT0 and check whether the output matches the following regular expressions:
eth1\s+egress\s+[1-9]\d*
eth1\s+ingress\s+[1-9]\d*
Show output
--------------------------------------------------------------
iface   mode    pkts match  pkts eval  bytes match  bytes eval
--------------------------------------------------------------
eth1   egress            9         17          576        1408
eth1   ingress          10         11          628         712
--------------------------------------------------------------
Total                   19         28         1204        2120
Example 3
Step 1: Set the following configuration in DUT0 :
set interfaces ethernet eth0 address 10.215.168.64/24
set interfaces ethernet eth1 address 192.168.1.1/24
set interfaces ethernet eth1 flow egress selector TCP_SEL
set interfaces ethernet eth1 flow ingress selector TCP_SEL
set system conntrack app-detect app-id-storage chained
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set system netflow app-id
set system netflow destination 10.215.168.1
set system netflow engine-id 1111
set traffic selector TCP_SEL rule 1 protocol tcp
Step 2: Set the following configuration in DUT1 :
set interfaces ethernet eth1 address 192.168.1.2/24
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
Step 3: Run the command system netflow show status on DUT0 and check whether the output matches the following regular expressions:
Protocol\sversion\s10\s\(ipfix\)
Export:.*Errors 0 pkts
sock0:\s127.0.0.1:2055,.*err: sndbuf reached 0, connect 0, cberr \d+, other 0
Show output
ipt_NETFLOW 2.6, srcversion 78C6C2B77E78F740D6A6F59; dir
Protocol version 10 (ipfix), refresh-rate 20, timeout-rate 30, (templates 0, active 1).
Timeouts: active 1800s, inactive 15s. Maxflows 2000000
Flows: active 0 (peak 2 reached 0d0h2m ago), mem 491K, worker delay 25/250 [1..25] (40 ms, 0 us, 0:0 [cpu1]).
Hash: size 62967 (mem 491K), metric 1.00 [1.00, 1.00, 1.00]. InHash: 0 pkt, 0 K, InPDU 0, 0.
Rate: 0 bits/sec, 0 packets/sec; Avg 1 min: 358 bps, 0 pps; 5 min: 388 bps, 0 pps
cpu#     pps; <search found new [metric], trunc frag alloc maxflows>, traffic: <pkt, bytes>, drop: <pkt, bytes>
Total      0;      0    153     20 [1.00],    0    0    0    0, traffic: 208, 0 MB, drop: 0, 0 K
cpu0       0;      0     24      8 [1.00],    0    0    0    0, traffic: 66, 0 MB, drop: 0, 0 K
cpu1       0;      0    110     12 [1.00],    0    0    0    0, traffic: 95, 0 MB, drop: 0, 0 K
cpu2       0;      0      3      0 [1.00],    0    0    0    0, traffic: 15, 0 MB, drop: 0, 0 K
cpu3       0;      0     16      0 [1.00],    0    0    0    0, traffic: 32, 0 MB, drop: 0, 0 K
Export: Rate 52 bytes/s; Total 34 pkts, 0 MB, 20 flows; Errors 0 pkts; Traffic lost 0 pkts, 0 Kbytes, 0 flows.
sock0: 127.0.0.1:2055, sndbuf 212992, filled 1, peak 1; err: sndbuf reached 0, connect 0, cberr 0, other 0
Step 4: Ping the IP address 192.168.1.2 from DUT0:
admin@DUT0$ ping 192.168.1.2 count 1 size 56 timeout 1Show output
PING 192.168.1.2 (192.168.1.2) 56(84) bytes of data.
64 bytes from 192.168.1.2: icmp_seq=1 ttl=64 time=0.492 ms

--- 192.168.1.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.492/0.492/0.492/0.000 ms
Step 5: Ping the IP address 10.215.168.1 from DUT0:
admin@DUT0$ ping 10.215.168.1 count 1 size 56 timeout 1Show output
PING 10.215.168.1 (10.215.168.1) 56(84) bytes of data.
64 bytes from 10.215.168.1: icmp_seq=1 ttl=64 time=0.191 ms

--- 10.215.168.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.191/0.191/0.191/0.000 ms
Step 6: Initiate a tcp connection from DUT1 to DUT0 and exchange messages between both endpoints
admin@DUT0$ monitor test connection server 8080 tcp
admin@DUT1$ monitor test connection client 192.168.1.1 8080 tcp
Step 7: Run the command system netflow show flows detailed on DUT0 and check whether the output matches the following regular expressions:
3\s+0\s+192.168.1.2:\d+\s+192.168.1.1:8080\s+6(\s+\S+){7}\s+[1-9]\d*
0\s+3\s+192.168.1.1:8080\s+192.168.1.2:\d+\s+6(\s+\S+){7}\s+[1-9]\d*
\s+L3:\d+;L4:8080\s+
Show output
------------------------------------------------------------------------------------------
Field       Description
------------------------------------------------------------------------------------------
#           Numeric flow identifier
hash        Hash of the flow
a           Shows if the flow is pending of being exported
iif         Input interface
oif         Output interface
src:port    Source IP:PORT
dst:port    Destination IP:PORT
protocol    Protocol identifier
nexthop     Next-hop
mark        Connmark
appid       AppIDs, as 'engine:selector' pairs
tos         Type of service identificator
tcpflags    TCP flags
options     Optional IP options
tcpoptions  TCP Options (MSS, Window Scaling, Selective Acknowledgements, Timestamps, Nop)
pkts        Packets counter
bytes       Bytes counter
ts_first    Timestamp of fist packet that passed through the flow
ts_last     Timestamp of last packet that passed through the flow


---------------------------------------------------------------------------------------------------------------------------------------------------------------------
#  hash  a  iif  oif  src:port           dst:port           protocol  nexthop  mark  appid         tos  tcpflags  options  tcpoptions  pkts  bytes  ts_first  ts_last
---------------------------------------------------------------------------------------------------------------------------------------------------------------------
1  5a89  0  0    3    192.168.1.1:8080   192.168.1.2:45248  6         0.0.0.0  0     L3:6;L4:8080  0x0  0x1b      0x0      0xf1000000  12    732    404       34
2  b9a2  0  3    0    192.168.1.2:45248  192.168.1.1:8080   6         0.0.0.0  0     L3:6;L4:8080  0x0  0x1b      0x0      0xf1000000  12    732    404       34
Step 8: Run the command system netflow show stats on DUT0 and check whether the output matches the following regular expressions:
eth1\s+egress\s+[1-9]\d*
eth1\s+ingress\s+[1-9]\d*
Show output
--------------------------------------------------------------
iface   mode    pkts match  pkts eval  bytes match  bytes eval
--------------------------------------------------------------
eth1   egress           12         20          732        1564
eth1   ingress          12         13          732         816
--------------------------------------------------------------
Total                   24         33         1464        2380
Example 4
Step 1: Set the following configuration in DUT0 :
set interfaces ethernet eth0 address 10.215.168.64/24
set interfaces ethernet eth1 address 192.168.1.1/24
set interfaces ethernet eth1 flow egress selector TCP_SEL
set interfaces ethernet eth1 flow ingress selector TCP_SEL
set interfaces ethernet eth1 traffic policy in MARK_POL
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set system netflow destination 10.215.168.1
set system netflow engine-id 1111
set traffic policy MARK_POL rule 1 set connmark 99
set traffic selector TCP_SEL rule 1 protocol tcp
Step 2: Set the following configuration in DUT1 :
set interfaces ethernet eth1 address 192.168.1.2/24
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
Step 3: Run the command system netflow show status on DUT0 and check whether the output matches the following regular expressions:
Protocol\sversion\s10\s\(ipfix\)
Export:.*Errors 0 pkts
sock0:\s127.0.0.1:2055,.*err: sndbuf reached 0, connect 0, cberr \d+, other 0
Show output
ipt_NETFLOW 2.6, srcversion 78C6C2B77E78F740D6A6F59; dir
Protocol version 10 (ipfix), refresh-rate 20, timeout-rate 30, (templates 0, active 1).
Timeouts: active 1800s, inactive 15s. Maxflows 2000000
Flows: active 0 (peak 2 reached 0d0h2m ago), mem 491K, worker delay 25/250 [1..25] (0 ms, 0 us, 0:0 [cpu0]).
Hash: size 62967 (mem 491K), metric 1.00 [1.00, 1.00, 1.00]. InHash: 0 pkt, 0 K, InPDU 0, 0.
Rate: 2584 bits/sec, 5 packets/sec; Avg 1 min: 634 bps, 0 pps; 5 min: 441 bps, 0 pps
cpu#     pps; <search found new [metric], trunc frag alloc maxflows>, traffic: <pkt, bytes>, drop: <pkt, bytes>
Total      4;      0    175     22 [1.00],    0    0    0    0, traffic: 232, 0 MB, drop: 0, 0 K
cpu0       1;      0     31      8 [1.00],    0    0    0    0, traffic: 73, 0 MB, drop: 0, 0 K
cpu1       3;      0    124     14 [1.00],    0    0    0    0, traffic: 111, 0 MB, drop: 0, 0 K
cpu2       0;      0      4      0 [1.00],    0    0    0    0, traffic: 16, 0 MB, drop: 0, 0 K
cpu3       0;      0     16      0 [1.00],    0    0    0    0, traffic: 32, 0 MB, drop: 0, 0 K
Export: Rate 0 bytes/s; Total 37 pkts, 0 MB, 20 flows; Errors 0 pkts; Traffic lost 24 pkts, 1 Kbytes, 2 flows.
sock0: 127.0.0.1:2055, sndbuf 212992, filled 1, peak 1; err: sndbuf reached 0, connect 0, cberr 0, other 0
Step 4: Ping the IP address 192.168.1.2 from DUT0:
admin@DUT0$ ping 192.168.1.2 count 1 size 56 timeout 1Show output
PING 192.168.1.2 (192.168.1.2) 56(84) bytes of data.
64 bytes from 192.168.1.2: icmp_seq=1 ttl=64 time=0.680 ms

--- 192.168.1.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.680/0.680/0.680/0.000 ms
Step 5: Ping the IP address 10.215.168.1 from DUT0:
admin@DUT0$ ping 10.215.168.1 count 1 size 56 timeout 1Show output
PING 10.215.168.1 (10.215.168.1) 56(84) bytes of data.
64 bytes from 10.215.168.1: icmp_seq=1 ttl=64 time=0.549 ms

--- 10.215.168.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.549/0.549/0.549/0.000 ms
Step 6: Initiate a tcp connection from DUT1 to DUT0 and exchange messages between both endpoints
admin@DUT0$ monitor test connection server 8080 tcp
admin@DUT1$ monitor test connection client 192.168.1.1 8080 tcp
Step 7: Run the command system netflow show flows detailed on DUT0 and check whether the output matches the following regular expressions:
3\s+0\s+192.168.1.2:\d+\s+192.168.1.1:8080\s+6\s+\S+\s+99(\s+\S+){5}\s+[1-9]\d*
0\s+3\s+192.168.1.1:8080\s+192.168.1.2:\d+\s+6\s+\S+\s+99(\s+\S+){5}\s+[1-9]\d*
Show output
------------------------------------------------------------------------------------------
Field       Description
------------------------------------------------------------------------------------------
#           Numeric flow identifier
hash        Hash of the flow
a           Shows if the flow is pending of being exported
iif         Input interface
oif         Output interface
src:port    Source IP:PORT
dst:port    Destination IP:PORT
protocol    Protocol identifier
nexthop     Next-hop
mark        Connmark
appid       AppIDs, as 'engine:selector' pairs
tos         Type of service identificator
tcpflags    TCP flags
options     Optional IP options
tcpoptions  TCP Options (MSS, Window Scaling, Selective Acknowledgements, Timestamps, Nop)
pkts        Packets counter
bytes       Bytes counter
ts_first    Timestamp of fist packet that passed through the flow
ts_last     Timestamp of last packet that passed through the flow


--------------------------------------------------------------------------------------------------------------------------------------------------------------
#  hash  a  iif  oif  src:port           dst:port           protocol  nexthop  mark  appid  tos  tcpflags  options  tcpoptions  pkts  bytes  ts_first  ts_last
--------------------------------------------------------------------------------------------------------------------------------------------------------------
1  d2be  0  3    0    192.168.1.2:45254  192.168.1.1:8080   6         0.0.0.0  99    -      0x0  0x1b      0x0      0xf1000000  10    628    387       35
2  abed  0  0    3    192.168.1.1:8080   192.168.1.2:45254  6         0.0.0.0  99    -      0x0  0x1b      0x0      0xf1000000  10    628    387       35
Step 8: Run the command system netflow show stats on DUT0 and check whether the output matches the following regular expressions:
eth1\s+egress\s+[1-9]\d*
eth1\s+ingress\s+[1-9]\d*
Show output
--------------------------------------------------------------
iface   mode    pkts match  pkts eval  bytes match  bytes eval
--------------------------------------------------------------
eth1   egress           10         16          628        1312
eth1   ingress          10         11          628         712
--------------------------------------------------------------
Total                   20         27         1256        2024