Site-To-Site
This scenario shows how to configure and connect two subnets with each other through a VPN tunnel set up between the two gateways. One end-point receives the local IP through DHCP.
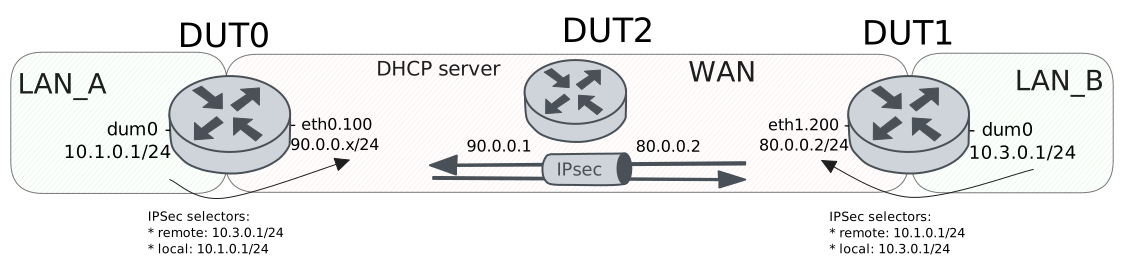
Test Site-To-Site Responder With Dynamic IP
Description
Simple VPN site-to-site configuration to
connect two subnets. DUT0 acts as a
responder so it only sets the tunnel up when
an incoming connection is received. Instead
of listening on a pre-configured IP address,
the local end-point IP is received through
DHCP.
Scenario
Step 1: Set the following configuration in DUT2 :
set interfaces ethernet eth0 vif 100 address 90.0.0.1/24
set interfaces ethernet eth1 vif 200 address 80.0.0.1/24
set service dhcp-server shared-network dhcpserver subnet 90.0.0.0/24 start 90.0.0.2 stop 90.0.0.2
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
Step 2: Set the following configuration in DUT0 :
set interfaces dummy dum0 address 10.1.0.1/24
set interfaces ethernet eth0 vif 100 address dhcp
set protocols static route 0.0.0.0/0 interface dum0
set protocols static route 80.0.0.0/24 next-hop 90.0.0.1
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk %any encrypted-secret U2FsdGVkX1+3u9EQvICP1CLEUEabYo/c8Qcudr4wYb4=
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id %any
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type respond
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER dhcp-interface eth0.100
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER remote-address 80.0.0.2
set vpn ipsec site-to-site peer PEER tunnel 1 local prefix 10.1.0.0/24
set vpn ipsec site-to-site peer PEER tunnel 1 local-interface dum0
set vpn ipsec site-to-site peer PEER tunnel 1 remote prefix 10.3.0.0/24
Step 3: Run the command interfaces ethernet eth0 vif 100 show on DUT0 and check whether the output contains the following tokens:
90.0.0.2Show output
---------------------------------------------------------------------
Name             IP Address           Admin  Oper  Vrf  Description
---------------------------------------------------------------------
eth0.100  90.0.0.2/24                   up     up
fe80::dcad:beff:feef:6c00/64
Step 4: Set the following configuration in DUT1 :
set interfaces dummy dum0 address 10.3.0.1/24
set interfaces ethernet eth1 vif 200 address 80.0.0.2/24
set protocols static route 0.0.0.0/0 interface dum0
set protocols static route 90.0.0.0/24 next-hop 80.0.0.1
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk %any encrypted-secret U2FsdGVkX1+A4+UxVPrcDf8XUnWf4y+KN/03AZQL7V8=
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id %any
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type initiate
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER local-address 80.0.0.2
set vpn ipsec site-to-site peer PEER remote-address 90.0.0.2
set vpn ipsec site-to-site peer PEER tunnel 1 local prefix 10.3.0.0/24
set vpn ipsec site-to-site peer PEER tunnel 1 local-interface dum0
set vpn ipsec site-to-site peer PEER tunnel 1 remote prefix 10.1.0.0/24
Step 5: Ping the IP address 80.0.0.2 from DUT0:
admin@DUT0$ ping 80.0.0.2 count 1 size 56 timeout 1Show output
PING 80.0.0.2 (80.0.0.2) 56(84) bytes of data.
64 bytes from 80.0.0.2: icmp_seq=1 ttl=63 time=0.490 ms

--- 80.0.0.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.490/0.490/0.490/0.000 ms
Step 6: Run the command vpn ipsec show sa on DUT1 and check whether the output matches the following regular expressions:
peer-PEER-tunnel-\d+.+INSTALLEDShow output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, cf300c3057915693_i* 240814fc111dec04_r
local  '80.0.0.2' @ 80.0.0.2[500]
remote '90.0.0.2' @ 90.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 0s ago, rekeying in 17201s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 0s ago, rekeying in 3397s, expires in 3960s
in  ce37c61b,      0 bytes,     0 packets
out c18f74ff,      0 bytes,     0 packets
local  10.3.0.0/24
remote 10.1.0.0/24
Step 7: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
peer-PEER-tunnel-\d+.+INSTALLEDShow output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, cf300c3057915693_i 240814fc111dec04_r*
local  '90.0.0.2' @ 90.0.0.2[500]
remote '80.0.0.2' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 0s ago, rekeying in 13889s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 0s ago, rekeying in 3467s, expires in 3960s
in  c18f74ff,      0 bytes,     0 packets
out ce37c61b,      0 bytes,     0 packets
local  10.1.0.0/24
remote 10.3.0.0/24
Step 8: Ping the IP address 10.1.0.1 from DUT1:
admin@DUT1$ ping 10.1.0.1 local-address 10.3.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.3.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.551 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.551/0.551/0.551/0.000 ms
Step 9: Ping the IP address 10.3.0.1 from DUT0:
admin@DUT0$ ping 10.3.0.1 local-address 10.1.0.1 count 1 size 56 timeout 1Show output
PING 10.3.0.1 (10.3.0.1) from 10.1.0.1 : 56(84) bytes of data.
64 bytes from 10.3.0.1: icmp_seq=1 ttl=64 time=0.537 ms

--- 10.3.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.537/0.537/0.537/0.000 ms
Step 10: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
[1-9]\d? packetsShow output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, cf300c3057915693_i 240814fc111dec04_r*
local  '90.0.0.2' @ 90.0.0.2[500]
remote '80.0.0.2' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 1s ago, rekeying in 13888s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 1s ago, rekeying in 3466s, expires in 3959s
in  c18f74ff,    168 bytes,     2 packets,     0s ago
out ce37c61b,    168 bytes,     2 packets,     0s ago
local  10.1.0.0/24
remote 10.3.0.0/24
Step 11: Run the command vpn ipsec show sa on DUT1 and check whether the output matches the following regular expressions:
[1-9]\d? packetsShow output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, cf300c3057915693_i* 240814fc111dec04_r
local  '80.0.0.2' @ 80.0.0.2[500]
remote '90.0.0.2' @ 90.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 1s ago, rekeying in 17200s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 1s ago, rekeying in 3396s, expires in 3959s
in  ce37c61b,    168 bytes,     2 packets,     0s ago
out c18f74ff,    168 bytes,     2 packets,     0s ago
local  10.3.0.0/24
remote 10.1.0.0/24
Attention
The command vpn show ipsec policy can be used to debug
the IPSec selectors that have been installed in OSDx devices.
Example for device DUT0:
Show output
src 10.1.0.0/24 dst 10.3.0.0/24 dev dum0
        dir out priority 375421
        tmpl src 90.0.0.2 dst 80.0.0.2
                proto esp spi 0xce37c61b reqid 1 mode tunnel
src 10.3.0.0/24 dst 10.1.0.0/24
        dir fwd priority 375423
        tmpl src 80.0.0.2 dst 90.0.0.2
                proto esp reqid 1 mode tunnel
src 10.3.0.0/24 dst 10.1.0.0/24
        dir in priority 375423
        tmpl src 80.0.0.2 dst 90.0.0.2
                proto esp reqid 1 mode tunnel
src 0.0.0.0/0 dst 0.0.0.0/0
        socket in priority 0
src 0.0.0.0/0 dst 0.0.0.0/0
        socket out priority 0
src 0.0.0.0/0 dst 0.0.0.0/0
        socket in priority 0
src 0.0.0.0/0 dst 0.0.0.0/0
        socket out priority 0
src ::/0 dst ::/0
        socket in priority 0
src ::/0 dst ::/0
        socket out priority 0
src ::/0 dst ::/0
        socket in priority 0
src ::/0 dst ::/0
        socket out priority 0
Test Site-To-Site Initiator With Dynamic IP
Description
Simple VPN site-to-site configuration to
connect two subnets. DUT0 acts as a initiator,
so it automatically attempts to start the tunnel
as soon as a local IP address is assigned
through DHCP.
Scenario
Step 1: Set the following configuration in DUT2 :
set interfaces ethernet eth0 vif 100 address 90.0.0.1/24
set interfaces ethernet eth1 vif 200 address 80.0.0.1/24
set service dhcp-server shared-network dhcpserver subnet 90.0.0.0/24 start 90.0.0.2 stop 90.0.0.2
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
Step 2: Set the following configuration in DUT1 :
set interfaces dummy dum0 address 10.3.0.1/24
set interfaces ethernet eth1 vif 200 address 80.0.0.2/24
set protocols static route 0.0.0.0/0 interface dum0
set protocols static route 90.0.0.0/24 next-hop 80.0.0.1
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk %any encrypted-secret U2FsdGVkX1+8SfwsPQIozdwCsTqt8lNYq5Nf5ucOz5c=
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id %any
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type respond
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER local-address 80.0.0.2
set vpn ipsec site-to-site peer PEER remote-address 90.0.0.2
set vpn ipsec site-to-site peer PEER tunnel 1 local prefix 10.3.0.0/24
set vpn ipsec site-to-site peer PEER tunnel 1 local-interface dum0
set vpn ipsec site-to-site peer PEER tunnel 1 remote prefix 10.1.0.0/24
Step 3: Set the following configuration in DUT0 :
set interfaces dummy dum0 address 10.1.0.1/24
set interfaces ethernet eth0 vif 100 address dhcp
set protocols static route 0.0.0.0/0 interface dum0
set protocols static route 80.0.0.0/24 next-hop 90.0.0.1
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk %any encrypted-secret U2FsdGVkX18WhoFWPFyDzKdPbmHXQtnnEns65Vy0x5c=
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id %any
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type initiate
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER dhcp-interface eth0.100
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER remote-address 80.0.0.2
set vpn ipsec site-to-site peer PEER tunnel 1 local prefix 10.1.0.0/24
set vpn ipsec site-to-site peer PEER tunnel 1 local-interface dum0
set vpn ipsec site-to-site peer PEER tunnel 1 remote prefix 10.3.0.0/24
Step 4: Run the command interfaces ethernet eth0 vif 100 show on DUT0 and check whether the output contains the following tokens:
90.0.0.2Show output
---------------------------------------------------------------------
Name             IP Address           Admin  Oper  Vrf  Description
---------------------------------------------------------------------
eth0.100  90.0.0.2/24                   up     up
fe80::dcad:beff:feef:6c00/64
Step 5: Ping the IP address 80.0.0.2 from DUT0:
admin@DUT0$ ping 80.0.0.2 count 1 size 56 timeout 1Show output
PING 80.0.0.2 (80.0.0.2) 56(84) bytes of data.
64 bytes from 80.0.0.2: icmp_seq=1 ttl=63 time=0.502 ms

--- 80.0.0.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.502/0.502/0.502/0.000 ms
Step 6: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
peer-PEER-tunnel-\d+.+INSTALLEDShow output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, a47c95b8b95e9a3a_i* 9235235ef815e71f_r
local  '90.0.0.2' @ 90.0.0.2[500]
remote '80.0.0.2' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 5s ago, rekeying in 24837s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 5s ago, rekeying in 3490s, expires in 3955s
in  ce993a33,      0 bytes,     0 packets
out c33c85cb,      0 bytes,     0 packets
local  10.1.0.0/24
remote 10.3.0.0/24
Step 7: Run the command vpn ipsec show sa on DUT1 and check whether the output matches the following regular expressions:
peer-PEER-tunnel-\d+.+INSTALLEDShow output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, a47c95b8b95e9a3a_i 9235235ef815e71f_r*
local  '80.0.0.2' @ 80.0.0.2[500]
remote '90.0.0.2' @ 90.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 5s ago, rekeying in 22690s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 5s ago, rekeying in 3281s, expires in 3955s
in  c33c85cb,      0 bytes,     0 packets
out ce993a33,      0 bytes,     0 packets
local  10.3.0.0/24
remote 10.1.0.0/24
Step 8: Ping the IP address 10.3.0.1 from DUT0:
admin@DUT0$ ping 10.3.0.1 local-address 10.1.0.1 count 1 size 56 timeout 1Show output
PING 10.3.0.1 (10.3.0.1) from 10.1.0.1 : 56(84) bytes of data.
64 bytes from 10.3.0.1: icmp_seq=1 ttl=64 time=0.927 ms

--- 10.3.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.927/0.927/0.927/0.000 ms
Step 9: Ping the IP address 10.1.0.1 from DUT1:
admin@DUT1$ ping 10.1.0.1 local-address 10.3.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.3.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.448 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.448/0.448/0.448/0.000 ms
Step 10: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
[1-9]\d? packetsShow output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, a47c95b8b95e9a3a_i* 9235235ef815e71f_r
local  '90.0.0.2' @ 90.0.0.2[500]
remote '80.0.0.2' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 5s ago, rekeying in 24837s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 5s ago, rekeying in 3490s, expires in 3955s
in  ce993a33,    168 bytes,     2 packets,     0s ago
out c33c85cb,    168 bytes,     2 packets,     0s ago
local  10.1.0.0/24
remote 10.3.0.0/24
Step 11: Run the command vpn ipsec show sa on DUT1 and check whether the output matches the following regular expressions:
[1-9]\d? packetsShow output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, a47c95b8b95e9a3a_i 9235235ef815e71f_r*
local  '80.0.0.2' @ 80.0.0.2[500]
remote '90.0.0.2' @ 90.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 6s ago, rekeying in 22689s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 6s ago, rekeying in 3280s, expires in 3954s
in  c33c85cb,    168 bytes,     2 packets,     0s ago
out ce993a33,    168 bytes,     2 packets,     0s ago
local  10.3.0.0/24
remote 10.1.0.0/24
Attention
The command vpn show ipsec policy can be used to debug
the IPSec selectors that have been installed in OSDx devices.
Example for device DUT0:
Show output
src 10.1.0.0/24 dst 10.3.0.0/24 dev dum0
        dir out priority 375421
        tmpl src 90.0.0.2 dst 80.0.0.2
                proto esp spi 0xc33c85cb reqid 1 mode tunnel
src 10.3.0.0/24 dst 10.1.0.0/24
        dir fwd priority 375423
        tmpl src 80.0.0.2 dst 90.0.0.2
                proto esp reqid 1 mode tunnel
src 10.3.0.0/24 dst 10.1.0.0/24
        dir in priority 375423
        tmpl src 80.0.0.2 dst 90.0.0.2
                proto esp reqid 1 mode tunnel
src 0.0.0.0/0 dst 0.0.0.0/0
        socket in priority 0
src 0.0.0.0/0 dst 0.0.0.0/0
        socket out priority 0
src 0.0.0.0/0 dst 0.0.0.0/0
        socket in priority 0
src 0.0.0.0/0 dst 0.0.0.0/0
        socket out priority 0
src ::/0 dst ::/0
        socket in priority 0
src ::/0 dst ::/0
        socket out priority 0
src ::/0 dst ::/0
        socket in priority 0
src ::/0 dst ::/0
        socket out priority 0