Site-To-Site
This scenario shows how to configure and connect two subnets with each other through a VPN tunnel. The initiator requests an additional IP address from the responder to use as the inner IPsec tunnel address.
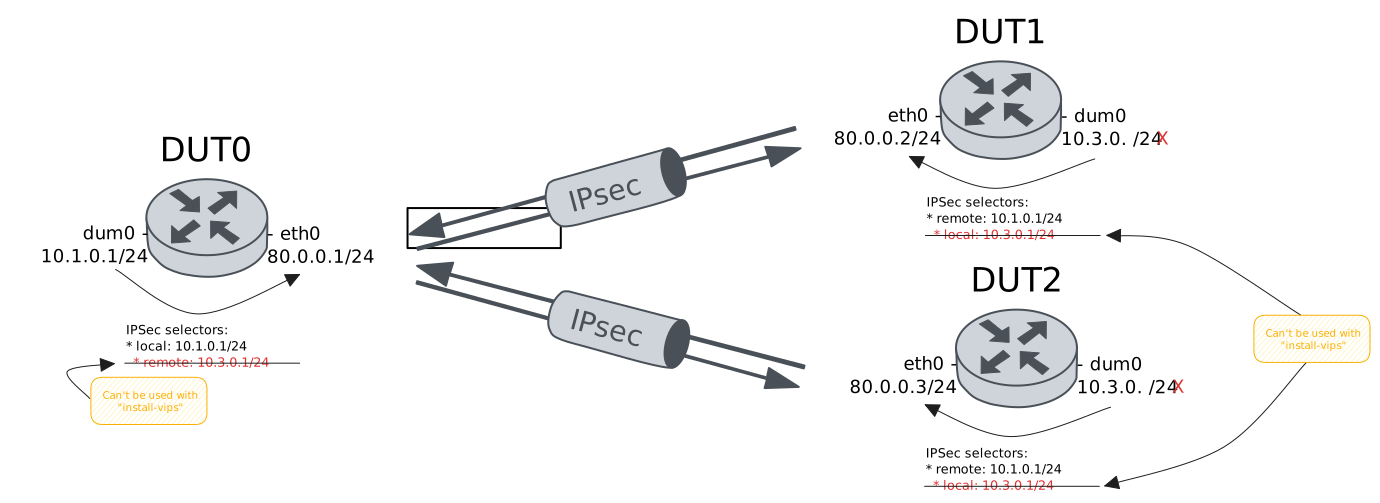
Test Site-To-Site VIP Pool And A Single Client
Description
In this scenario, DUT1 acts as initiator
and requests a VIP from the DUT0 pool.
Scenario
Step 1: Set the following configuration in DUT0 :
set interfaces dummy dum0 address 10.1.0.1/24
set interfaces ethernet eth0 address 80.0.0.1/24
set protocols static route 10.3.0.0/24 interface eth0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk %any encrypted-secret U2FsdGVkX1/YPZ9uvS4KvIVm/t0r57yyeBjIpeMLn/g=
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id %any
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec pool POOL prefix 10.3.0.0/24
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type respond
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER pool POOL
set vpn ipsec site-to-site peer PEER tunnel 1 local prefix 10.1.0.0/24
Step 2: Set the following configuration in DUT1 :
set interfaces dummy dum0
set interfaces ethernet eth0 address 80.0.0.2/24
set protocols static route 10.1.0.0/24 interface eth0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk %any encrypted-secret U2FsdGVkX18inswCcUH+WpdKBdK9clPPq/TzAqpRkLY=
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id %any
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type initiate
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER install-vips interface dum0
set vpn ipsec site-to-site peer PEER remote-address 80.0.0.1
set vpn ipsec site-to-site peer PEER tunnel 1 remote prefix 10.1.0.0/24
Step 3: Ping the IP address 80.0.0.1 from DUT1:
admin@DUT1$ ping 80.0.0.1 count 1 size 56 timeout 1Show output
PING 80.0.0.1 (80.0.0.1) 56(84) bytes of data.
64 bytes from 80.0.0.1: icmp_seq=1 ttl=64 time=2.47 ms

--- 80.0.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 2.467/2.467/2.467/0.000 ms
Step 4: Ping the IP address 80.0.0.2 from DUT0:
admin@DUT0$ ping 80.0.0.2 count 1 size 56 timeout 1Show output
PING 80.0.0.2 (80.0.0.2) 56(84) bytes of data.
64 bytes from 80.0.0.2: icmp_seq=1 ttl=64 time=1.46 ms

--- 80.0.0.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 1.457/1.457/1.457/0.000 ms
Step 5: Run the command vpn ipsec show sa on DUT1 and check whether the output matches the following regular expressions:
peer-PEER-tunnel-\d+.+INSTALLEDShow output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, 56062fabbce61268_i* f44e9005aa8895a2_r
local  '80.0.0.2' @ 80.0.0.2[4500] [10.3.0.1]
remote '80.0.0.1' @ 80.0.0.1[4500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 1s ago, rekeying in 18129s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL-in-UDP, ESP:AES_GCM_16-256
installed 1s ago, rekeying in 3387s, expires in 3959s
in  c505fcdf,      0 bytes,     0 packets
out c47f3ac6,      0 bytes,     0 packets
local  10.3.0.1/32
remote 10.1.0.0/24
Step 6: Run the command interfaces dummy dum0 show on DUT1 and expect the following output:
Show output
-----------------------------------------------------------------
Name           IP Address           Admin  Oper  Vrf  Description
-----------------------------------------------------------------
dum0  10.3.0.1/32                   up     up
      fe80::3017:aeff:fe15:ba10/64
Step 7: Ping the IP address 10.1.0.1 from DUT1:
admin@DUT1$ ping 10.1.0.1 local-address 10.3.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.3.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=2.07 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 2.073/2.073/2.073/0.000 ms
Step 8: Initiate a tcp connection from DUT1 to DUT0 and exchange messages between both endpoints
admin@DUT0$ monitor test connection server 8080 tcp
admin@DUT1$ monitor test connection client 10.1.0.1 8080 tcp local-address 10.3.0.1
Step 9: Run the command vpn ipsec show sa on DUT1 and check whether the output matches the following regular expressions:
[1-9]\d? packetsShow output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, 56062fabbce61268_i* f44e9005aa8895a2_r
local  '80.0.0.2' @ 80.0.0.2[4500] [10.3.0.1]
remote '80.0.0.1' @ 80.0.0.1[4500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 4s ago, rekeying in 18126s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL-in-UDP, ESP:AES_GCM_16-256
installed 4s ago, rekeying in 3384s, expires in 3956s
in  c505fcdf,    660 bytes,    10 packets,     0s ago
out c47f3ac6,    712 bytes,    11 packets,     0s ago
local  10.3.0.1/32
remote 10.1.0.0/24
Step 10: Run the command vpn ipsec show pool summary on DUT0 and check whether the output matches the following regular expressions:
1\s+0\s+\d+Show output
--------------------------------------
pool  base IP   online  offline  total
--------------------------------------
POOL  10.3.0.0       1        0    254
Test Site-To-Site VIP Pool And A Single Client Using On-Demand Connection-Type
Description
In this scenario, DUT1 requests a VIP from
the DUT0 pool. Both devices use
on-demand as a connection-type.
Scenario
Step 1: Set the following configuration in DUT0 :
set interfaces dummy dum0 address 10.1.0.1/24
set interfaces ethernet eth0 address 80.0.0.1/24
set protocols static route 10.3.0.0/24 interface eth0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk %any encrypted-secret U2FsdGVkX1+88xT0Ax/Zl7ooPXRvAlZeQw2h4vi90eU=
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id %any
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec pool POOL prefix 10.3.0.0/24
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type on-demand
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER pool POOL
set vpn ipsec site-to-site peer PEER tunnel 1 local prefix 10.1.0.0/24
Step 2: Set the following configuration in DUT1 :
set interfaces dummy dum0
set interfaces ethernet eth0 address 80.0.0.2/24
set protocols static route 10.1.0.0/24 interface eth0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk %any encrypted-secret U2FsdGVkX1/w7rnFLXDOSBfHQkecIgxWoSMrs+EN19o=
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id %any
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type on-demand
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER install-vips interface dum0
set vpn ipsec site-to-site peer PEER remote-address 80.0.0.1
set vpn ipsec site-to-site peer PEER tunnel 1 remote prefix 10.1.0.0/24
Step 3: Ping the IP address 80.0.0.1 from DUT1:
admin@DUT1$ ping 80.0.0.1 count 1 size 56 timeout 1Show output
PING 80.0.0.1 (80.0.0.1) 56(84) bytes of data.
64 bytes from 80.0.0.1: icmp_seq=1 ttl=64 time=0.540 ms

--- 80.0.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.540/0.540/0.540/0.000 ms
Step 4: Ping the IP address 80.0.0.2 from DUT0:
admin@DUT0$ ping 80.0.0.2 count 1 size 56 timeout 1Show output
PING 80.0.0.2 (80.0.0.2) 56(84) bytes of data.
64 bytes from 80.0.0.2: icmp_seq=1 ttl=64 time=0.521 ms

--- 80.0.0.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.521/0.521/0.521/0.000 ms
Step 5: Expect a failure in the following command:
Ping the IP address 10.1.0.1 from DUT1:
admin@DUT1$ ping 10.1.0.1 count 5 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) 56(84) bytes of data.

--- 10.1.0.1 ping statistics ---
5 packets transmitted, 0 received, 100% packet loss, time 4102ms
Step 6: Run the command vpn ipsec show sa on DUT1 and check whether the output matches the following regular expressions:
peer-PEER-tunnel-\d+.+INSTALLEDShow output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, 0cf77279bf4ca9db_i* 0a88d0c75e12ddf9_r
local  '80.0.0.2' @ 80.0.0.2[4500] [10.3.0.1]
remote '80.0.0.1' @ 80.0.0.1[4500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 5s ago, rekeying in 21897s
peer-PEER-tunnel-1: #2, reqid 1, INSTALLED, TUNNEL-in-UDP, ESP:AES_GCM_16-256
installed 5s ago, rekeying in 3338s, expires in 3955s
in  c381520e,      0 bytes,     0 packets
out c8b9acc8,    336 bytes,     4 packets,     2s ago
local  10.3.0.1/32
remote 10.1.0.0/24
Step 7: Run the command interfaces dummy dum0 show on DUT1 and expect the following output:
Show output
-----------------------------------------------------------------
Name           IP Address           Admin  Oper  Vrf  Description
-----------------------------------------------------------------
dum0  10.3.0.1/32                   up     up
      fe80::a876:9fff:fe81:31dd/64
Step 8: Ping the IP address 10.1.0.1 from DUT1:
admin@DUT1$ ping 10.1.0.1 local-address 10.3.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.3.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=3.86 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 3.857/3.857/3.857/0.000 ms
Step 9: Initiate a tcp connection from DUT1 to DUT0 and exchange messages between both endpoints
admin@DUT0$ monitor test connection server 8080 tcp
admin@DUT1$ monitor test connection client 10.1.0.1 8080 tcp local-address 10.3.0.1
Step 10: Run the command vpn ipsec show sa on DUT1 and check whether the output matches the following regular expressions:
[1-9]\d? packetsShow output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, 0cf77279bf4ca9db_i* 0a88d0c75e12ddf9_r
local  '80.0.0.2' @ 80.0.0.2[4500] [10.3.0.1]
remote '80.0.0.1' @ 80.0.0.1[4500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 8s ago, rekeying in 21894s
peer-PEER-tunnel-1: #2, reqid 1, INSTALLED, TUNNEL-in-UDP, ESP:AES_GCM_16-256
installed 8s ago, rekeying in 3335s, expires in 3952s
in  c381520e,    868 bytes,    14 packets,     1s ago
out c8b9acc8,   1204 bytes,    18 packets,     1s ago
local  10.3.0.1/32
remote 10.1.0.0/24
Step 11: Run the command vpn ipsec show pool summary on DUT0 and check whether the output matches the following regular expressions:
1\s+0\s+\d+Show output
--------------------------------------
pool  base IP   online  offline  total
--------------------------------------
POOL  10.3.0.0       1        0    254
Test Site-To-Site VIP Pool And Multiple Clients
Description
In this scenario, DUT0 install routes
in a separate VRF called LAN.
Scenario
Step 1: Set the following configuration in DUT0 :
set interfaces dummy dum0 address 10.1.0.1/24
set interfaces ethernet eth0 address 80.0.0.1/24
set protocols static route 10.3.0.0/24 interface eth0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk %any encrypted-secret U2FsdGVkX1+N1hLLsAVvTE2cfIVQYUlNOS6I/kIixYc=
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id %any
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec pool POOL prefix 10.3.0.0/24
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type respond
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER pool POOL
set vpn ipsec site-to-site peer PEER tunnel 1 local prefix 10.1.0.0/24
Step 2: Set the following configuration in DUT1 :
set interfaces dummy dum0
set interfaces ethernet eth0 address 80.0.0.2/24
set protocols static route 10.1.0.0/24 interface eth0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk %any encrypted-secret U2FsdGVkX1/kRkJvSYfTXN7sHe7CjpmTffBFwW9im/I=
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id %any
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type initiate
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER install-vips interface dum0
set vpn ipsec site-to-site peer PEER remote-address 80.0.0.1
set vpn ipsec site-to-site peer PEER tunnel 1 remote prefix 10.1.0.0/24
Step 3: Ping the IP address 80.0.0.1 from DUT1:
admin@DUT1$ ping 80.0.0.1 count 1 size 56 timeout 1Show output
PING 80.0.0.1 (80.0.0.1) 56(84) bytes of data.
64 bytes from 80.0.0.1: icmp_seq=1 ttl=64 time=0.363 ms

--- 80.0.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.363/0.363/0.363/0.000 ms
Step 4: Ping the IP address 80.0.0.2 from DUT0:
admin@DUT0$ ping 80.0.0.2 count 1 size 56 timeout 1Show output
PING 80.0.0.2 (80.0.0.2) 56(84) bytes of data.
64 bytes from 80.0.0.2: icmp_seq=1 ttl=64 time=0.245 ms

--- 80.0.0.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.245/0.245/0.245/0.000 ms
Step 5: Set the following configuration in DUT2 :
set interfaces dummy dum0
set interfaces ethernet eth0 address 80.0.0.3/24
set protocols static route 10.1.0.0/24 interface eth0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk %any encrypted-secret U2FsdGVkX18rjR/62JEVEO5kydQxs5taBj3BoBIdrXg=
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id %any
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER install-vips interface dum0
set vpn ipsec site-to-site peer PEER remote-address 80.0.0.1
set vpn ipsec site-to-site peer PEER tunnel 1 remote prefix 10.1.0.0/24
Step 6: Run the command vpn ipsec show sa on DUT1 and check whether the output matches the following regular expressions:
peer-PEER-tunnel-\d+.+INSTALLEDShow output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, a305ec26bdec34c4_i* ad5aa92f25534f0c_r
local  '80.0.0.2' @ 80.0.0.2[4500] [10.3.0.1]
remote '80.0.0.1' @ 80.0.0.1[4500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 4s ago, rekeying in 16951s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL-in-UDP, ESP:AES_GCM_16-256
installed 4s ago, rekeying in 3265s, expires in 3956s
in  c02965be,      0 bytes,     0 packets
out c51ecd20,      0 bytes,     0 packets
local  10.3.0.1/32
remote 10.1.0.0/24
Step 7: Run the command interfaces dummy dum0 show on DUT1 and expect the following output:
Show output
-----------------------------------------------------------------
Name           IP Address           Admin  Oper  Vrf  Description
-----------------------------------------------------------------
dum0  10.3.0.1/32                   up     up
      fe80::3017:aeff:fe15:ba10/64
Step 8: Ping the IP address 10.1.0.1 from DUT1:
admin@DUT1$ ping 10.1.0.1 local-address 10.3.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.3.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.563 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.563/0.563/0.563/0.000 ms
Step 9: Initiate a tcp connection from DUT1 to DUT0 and exchange messages between both endpoints
admin@DUT0$ monitor test connection server 8080 tcp
admin@DUT1$ monitor test connection client 10.1.0.1 8080 tcp local-address 10.3.0.1
Step 10: Run the command vpn ipsec show sa on DUT1 and check whether the output matches the following regular expressions:
[1-9]\d? packetsShow output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, a305ec26bdec34c4_i* ad5aa92f25534f0c_r
local  '80.0.0.2' @ 80.0.0.2[4500] [10.3.0.1]
remote '80.0.0.1' @ 80.0.0.1[4500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 7s ago, rekeying in 16948s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL-in-UDP, ESP:AES_GCM_16-256
installed 7s ago, rekeying in 3262s, expires in 3953s
in  c02965be,    660 bytes,    10 packets,     1s ago
out c51ecd20,    764 bytes,    12 packets,     1s ago
local  10.3.0.1/32
remote 10.1.0.0/24
Step 11: Run the command vpn ipsec show sa on DUT2 and check whether the output matches the following regular expressions:
peer-PEER-tunnel-\d+.+INSTALLEDShow output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, 88b93ae730140c13_i* 60d214f23d72453b_r
local  '80.0.0.3' @ 80.0.0.3[4500] [10.3.0.2]
remote '80.0.0.1' @ 80.0.0.1[4500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 4s ago, rekeying in 17279s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL-in-UDP, ESP:AES_GCM_16-256
installed 4s ago, rekeying in 3493s, expires in 3956s
in  c4090502,      0 bytes,     0 packets
out c558d233,      0 bytes,     0 packets
local  10.3.0.2/32
remote 10.1.0.0/24
Step 12: Run the command interfaces dummy dum0 show on DUT2 and expect the following output:
Show output
-----------------------------------------------------------------
Name           IP Address           Admin  Oper  Vrf  Description
-----------------------------------------------------------------
dum0  10.3.0.2/32                   up     up
      fe80::64e6:91ff:fe2e:3e6c/64
Step 13: Ping the IP address 10.1.0.1 from DUT2:
admin@DUT2$ ping 10.1.0.1 local-address 10.3.0.2 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.3.0.2 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.868 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.868/0.868/0.868/0.000 ms
Step 14: Initiate a tcp connection from DUT2 to DUT0 and exchange messages between both endpoints
admin@DUT0$ monitor test connection server 8080 tcp
admin@DUT2$ monitor test connection client 10.1.0.1 8080 tcp local-address 10.3.0.2
Step 15: Run the command vpn ipsec show sa on DUT2 and check whether the output matches the following regular expressions:
[1-9]\d? packetsShow output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, 88b93ae730140c13_i* 60d214f23d72453b_r
local  '80.0.0.3' @ 80.0.0.3[4500] [10.3.0.2]
remote '80.0.0.1' @ 80.0.0.1[4500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 7s ago, rekeying in 17276s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL-in-UDP, ESP:AES_GCM_16-256
installed 7s ago, rekeying in 3490s, expires in 3953s
in  c4090502,    660 bytes,    10 packets,     1s ago
out c558d233,    816 bytes,    13 packets,     1s ago
local  10.3.0.2/32
remote 10.1.0.0/24
Step 16: Run the command vpn ipsec show pool summary on DUT0 and check whether the output matches the following regular expressions:
2\s+0\s+\d+Show output
--------------------------------------
pool  base IP   online  offline  total
--------------------------------------
POOL  10.3.0.0       2        0    254