Roadwarrior
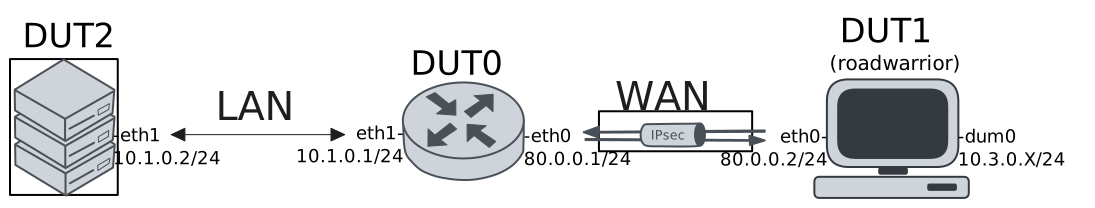
This scenario shows different ways to setup a roadwarrior VPN connection; in which, instead of using a N2N (network to network) connection, a single machine (e.g., a host) is able to connect to a remote private network.
On the one hand, DUT2 and DUT0 represent a remote branch
office. On the other hand, DUT1 is a roadwarrior that can
establish a connection to DUT2 using different virtual IPs.
Note that security associations (SAs) have to be manually
flushed with the command clear vpn ipsec sa. Depending on
the configuration parameter connection-type, the new tunnel
connections will be created or not.
Test VPN Roadwarrior Connection With VTI
Description
In this scenario, DUT0 uses a VTI
interface to encapsulate the VPN traffic.
Scenario
Step 1: Set the following configuration in DUT2 :
set interfaces ethernet eth1 address 10.1.0.2/24
set protocols static route 0.0.0.0/0 next-hop 10.1.0.1
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
Step 2: Set the following configuration in DUT0 :
set interfaces ethernet eth0 address 80.0.0.1/24
set interfaces ethernet eth1 address 10.1.0.1/24
set interfaces vti vti0 ipsec PEER
set interfaces vti vti0 local-address 80.0.0.1
set interfaces vti vti0 remote-address 0.0.0.0
set protocols static route 10.3.0.0/24 interface vti0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk %any encrypted-secret U2FsdGVkX18hiQo/xm+x87QaNytERzQdSbbuE8bgo1k=
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id %any
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type respond
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER local-address 80.0.0.1
set vpn ipsec site-to-site peer PEER vti local prefix 10.1.0.0/24
Step 3: Set the following configuration in DUT1 :
set interfaces dummy dum0 address 10.3.0.1/24
set interfaces ethernet eth0 address 80.0.0.2/24
set protocols static route 10.1.0.0/24 interface eth0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk %any encrypted-secret U2FsdGVkX19xz0zCU+VsckkKoBz6uPEybX1KpH1LXVQ=
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id %any
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec logging log-types any log-level 1
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type initiate
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER remote-address 80.0.0.1
set vpn ipsec site-to-site peer PEER tunnel 1 remote prefix 10.1.0.0/24
Step 4: Ping the IP address 80.0.0.1 from DUT1:
admin@DUT1$ ping 80.0.0.1 count 1 size 56 timeout 1Show output
PING 80.0.0.1 (80.0.0.1) 56(84) bytes of data.
64 bytes from 80.0.0.1: icmp_seq=1 ttl=64 time=0.521 ms

--- 80.0.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.521/0.521/0.521/0.000 ms
Step 5: Ping the IP address 80.0.0.2 from DUT0:
admin@DUT0$ ping 80.0.0.2 count 1 size 56 timeout 1Show output
PING 80.0.0.2 (80.0.0.2) 56(84) bytes of data.
64 bytes from 80.0.0.2: icmp_seq=1 ttl=64 time=0.330 ms

--- 80.0.0.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.330/0.330/0.330/0.000 ms
Step 6: Ping the IP address 10.1.0.2 from DUT0:
admin@DUT0$ ping 10.1.0.2 count 1 size 56 timeout 1Show output
PING 10.1.0.2 (10.1.0.2) 56(84) bytes of data.
64 bytes from 10.1.0.2: icmp_seq=1 ttl=64 time=0.554 ms

--- 10.1.0.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.554/0.554/0.554/0.000 ms
Step 7: Run the command interfaces dummy dum0 show on DUT1 and expect the following output:
Show output
-----------------------------------------------------------------
Name           IP Address           Admin  Oper  Vrf  Description
-----------------------------------------------------------------
dum0  10.3.0.1/24                   up     up
      fe80::3017:aeff:fe15:ba10/64
Step 8: Ping the IP address 10.1.0.1 from DUT1:
admin@DUT1$ ping 10.1.0.1 local-address 10.3.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.3.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.736 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.736/0.736/0.736/0.000 ms
Step 9: Ping the IP address 10.1.0.2 from DUT1:
admin@DUT1$ ping 10.1.0.2 local-address 10.3.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.2 (10.1.0.2) from 10.3.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.2: icmp_seq=1 ttl=63 time=0.942 ms

--- 10.1.0.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.942/0.942/0.942/0.000 ms
Step 10: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
[1-9]\d? packetsShow output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, bd122625a0c78f42_i 86270c99ae4f087d_r*
local  '80.0.0.1' @ 80.0.0.1[4500]
remote '80.0.0.2' @ 80.0.0.2[4500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 1s ago, rekeying in 24782s
peer-PEER-tunnel-VTI: #1, reqid 1, INSTALLED, TUNNEL-in-UDP, ESP:AES_GCM_16-256
installed 1s ago, rekeying in 3478s, expires in 3959s
in  c795eae1 (0x90000000),    168 bytes,     2 packets,     0s ago
out c5a2b13e (0x90000000),    168 bytes,     2 packets,     0s ago
local  10.1.0.0/24
remote 0.0.0.0/0
Step 11: Run the command vpn ipsec clear sa on DUT1 and expect the following output:
Show output
Closed tunnels: 1
Step 12: Modify the following configuration lines in DUT1 :
delete interfaces dummy dum0 address 10.3.0.1/24
set interfaces dummy dum0 address 10.3.0.2/24
Step 13: Run the command vpn ipsec initiate peer PEER on DUT1 and expect the following output:
Show output
Initiated tunnels: 1
Step 14: Run the command interfaces dummy dum0 show on DUT1 and expect the following output:
Show output
-----------------------------------------------------------------
Name           IP Address           Admin  Oper  Vrf  Description
-----------------------------------------------------------------
dum0  10.3.0.2/24                   up     up
      fe80::3017:aeff:fe15:ba10/64
Step 15: Ping the IP address 10.1.0.1 from DUT1:
admin@DUT1$ ping 10.1.0.1 local-address 10.3.0.2 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.3.0.2 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.690 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.690/0.690/0.690/0.000 ms
Step 16: Ping the IP address 10.1.0.2 from DUT1:
admin@DUT1$ ping 10.1.0.2 local-address 10.3.0.2 count 1 size 56 timeout 1Show output
PING 10.1.0.2 (10.1.0.2) from 10.3.0.2 : 56(84) bytes of data.
64 bytes from 10.1.0.2: icmp_seq=1 ttl=63 time=0.870 ms

--- 10.1.0.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.870/0.870/0.870/0.000 ms
Step 17: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
[1-9]\d? packetsShow output
vpn-peer-PEER: #2, ESTABLISHED, IKEv2, e4c7fa723716bd17_i fc1d282fb8cbe95e_r*
local  '80.0.0.1' @ 80.0.0.1[4500]
remote '80.0.0.2' @ 80.0.0.2[4500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 0s ago, rekeying in 20791s
peer-PEER-tunnel-VTI: #2, reqid 1, INSTALLED, TUNNEL-in-UDP, ESP:AES_GCM_16-256
installed 0s ago, rekeying in 3385s, expires in 3960s
in  c82e8fd9 (0x90000000),    168 bytes,     2 packets,     0s ago
out c011bec3 (0x90000000),    168 bytes,     2 packets,     0s ago
local  10.1.0.0/24
remote 0.0.0.0/0
Test VPN Roadwarrior Connection With Global Policies
Description
In this scenario, DUT0 uses global VPN
policies (or selectors) to encapsulate traffic.
Scenario
Step 1: Set the following configuration in DUT2 :
set interfaces ethernet eth1 address 10.1.0.2/24
set protocols static route 0.0.0.0/0 next-hop 10.1.0.1
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
Step 2: Set the following configuration in DUT0 :
set interfaces ethernet eth0 address 80.0.0.1/24
set interfaces ethernet eth1 address 10.1.0.1/24
set protocols static route 10.3.0.0/24 interface eth0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk %any encrypted-secret U2FsdGVkX18tNECEFmLaqUGIlm7yyU9nuS9QwWn/QM8=
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id %any
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type respond
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER local-address 80.0.0.1
set vpn ipsec site-to-site peer PEER tunnel 1 local prefix 10.1.0.0/24
set vpn ipsec site-to-site peer PEER tunnel 1 remote prefix 10.3.0.0/24
Step 3: Set the following configuration in DUT1 :
set interfaces dummy dum0 address 10.3.0.1/24
set interfaces ethernet eth0 address 80.0.0.2/24
set protocols static route 10.1.0.0/24 interface eth0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk %any encrypted-secret U2FsdGVkX18VTD3NDwBQ/j3jOIVXKYdfiiHtXHLtk0A=
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id %any
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec logging log-types any log-level 1
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type initiate
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER remote-address 80.0.0.1
set vpn ipsec site-to-site peer PEER tunnel 1 remote prefix 10.1.0.0/24
Step 4: Ping the IP address 80.0.0.1 from DUT1:
admin@DUT1$ ping 80.0.0.1 count 1 size 56 timeout 1Show output
PING 80.0.0.1 (80.0.0.1) 56(84) bytes of data.
64 bytes from 80.0.0.1: icmp_seq=1 ttl=64 time=0.664 ms

--- 80.0.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.664/0.664/0.664/0.000 ms
Step 5: Ping the IP address 80.0.0.2 from DUT0:
admin@DUT0$ ping 80.0.0.2 count 1 size 56 timeout 1Show output
PING 80.0.0.2 (80.0.0.2) 56(84) bytes of data.
64 bytes from 80.0.0.2: icmp_seq=1 ttl=64 time=0.323 ms

--- 80.0.0.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.323/0.323/0.323/0.000 ms
Step 6: Ping the IP address 10.1.0.2 from DUT0:
admin@DUT0$ ping 10.1.0.2 count 1 size 56 timeout 1Show output
PING 10.1.0.2 (10.1.0.2) 56(84) bytes of data.
64 bytes from 10.1.0.2: icmp_seq=1 ttl=64 time=0.341 ms

--- 10.1.0.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.341/0.341/0.341/0.000 ms
Step 7: Run the command interfaces dummy dum0 show on DUT1 and expect the following output:
Show output
-----------------------------------------------------------------
Name           IP Address           Admin  Oper  Vrf  Description
-----------------------------------------------------------------
dum0  10.3.0.1/24                   up     up
      fe80::3017:aeff:fe15:ba10/64
Step 8: Ping the IP address 10.1.0.1 from DUT1:
admin@DUT1$ ping 10.1.0.1 local-address 10.3.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.3.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.381 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.381/0.381/0.381/0.000 ms
Step 9: Ping the IP address 10.1.0.2 from DUT1:
admin@DUT1$ ping 10.1.0.2 local-address 10.3.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.2 (10.1.0.2) from 10.3.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.2: icmp_seq=1 ttl=63 time=0.518 ms

--- 10.1.0.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.518/0.518/0.518/0.000 ms
Step 10: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
[1-9]\d? packetsShow output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, 5bc5e08b4d79d995_i 3d4eeebd44c8cffb_r*
local  '80.0.0.1' @ 80.0.0.1[4500]
remote '80.0.0.2' @ 80.0.0.2[4500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 1s ago, rekeying in 15272s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL-in-UDP, ESP:AES_GCM_16-256
installed 1s ago, rekeying in 3316s, expires in 3959s
in  c71b23d3,    168 bytes,     2 packets,     0s ago
out cd506f06,    168 bytes,     2 packets,     0s ago
local  10.1.0.0/24
remote 10.3.0.0/24
Step 11: Run the command vpn ipsec clear sa on DUT1 and expect the following output:
Show output
Closed tunnels: 1
Step 12: Modify the following configuration lines in DUT1 :
delete interfaces dummy dum0 address 10.3.0.1/24
set interfaces dummy dum0 address 10.3.0.2/24
Step 13: Run the command vpn ipsec initiate peer PEER on DUT1 and expect the following output:
Show output
Initiated tunnels: 1
Step 14: Run the command interfaces dummy dum0 show on DUT1 and expect the following output:
Show output
-----------------------------------------------------------------
Name           IP Address           Admin  Oper  Vrf  Description
-----------------------------------------------------------------
dum0  10.3.0.2/24                   up     up
      fe80::3017:aeff:fe15:ba10/64
Step 15: Ping the IP address 10.1.0.1 from DUT1:
admin@DUT1$ ping 10.1.0.1 local-address 10.3.0.2 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.3.0.2 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.555 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.555/0.555/0.555/0.000 ms
Step 16: Ping the IP address 10.1.0.2 from DUT1:
admin@DUT1$ ping 10.1.0.2 local-address 10.3.0.2 count 1 size 56 timeout 1Show output
PING 10.1.0.2 (10.1.0.2) from 10.3.0.2 : 56(84) bytes of data.
64 bytes from 10.1.0.2: icmp_seq=1 ttl=63 time=0.974 ms

--- 10.1.0.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.974/0.974/0.974/0.000 ms
Step 17: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
[1-9]\d? packetsShow output
vpn-peer-PEER: #2, ESTABLISHED, IKEv2, 8769daf2f234a0ad_i b3287607cb9bb963_r*
local  '80.0.0.1' @ 80.0.0.1[4500]
remote '80.0.0.2' @ 80.0.0.2[4500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 0s ago, rekeying in 24120s
peer-PEER-tunnel-1: #2, reqid 1, INSTALLED, TUNNEL-in-UDP, ESP:AES_GCM_16-256
installed 0s ago, rekeying in 3332s, expires in 3960s
in  c09c4eb8,    168 bytes,     2 packets,     1s ago
out c60e0080,    168 bytes,     2 packets,     1s ago
local  10.1.0.0/24
remote 10.3.0.0/24
Test VPN Roadwarrior Connection With VTI And VIPs Pool
Description
In this scenario, DUT0 uses a VTI
interface to encapsulate the VPN traffic.
DUT1 requests a virtual IP address from
DUT0 and it installed in dum0. Routes are
also automatically installed taking into
account the negotiated selectors.
Scenario
Step 1: Set the following configuration in DUT2 :
set interfaces ethernet eth1 address 10.1.0.2/24
set protocols static route 0.0.0.0/0 next-hop 10.1.0.1
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
Step 2: Set the following configuration in DUT0 :
set interfaces ethernet eth0 address 80.0.0.1/24
set interfaces ethernet eth1 address 10.1.0.1/24
set interfaces vti vti0 ipsec PEER
set interfaces vti vti0 local-address 80.0.0.1
set interfaces vti vti0 remote-address 0.0.0.0
set protocols static route 10.3.0.0/24 interface vti0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk %any encrypted-secret U2FsdGVkX19Sz9HQIV0M/iBCXaUDMs3ni+4Cwj0OVd8=
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id %any
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec pool POOL prefix 10.3.0.0/24
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type respond
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER local-address 80.0.0.1
set vpn ipsec site-to-site peer PEER pool POOL
set vpn ipsec site-to-site peer PEER vti local prefix 10.1.0.0/24
Step 3: Set the following configuration in DUT1 :
set interfaces dummy dum0
set interfaces ethernet eth0 address 80.0.0.2/24
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set system vrf main
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk %any encrypted-secret U2FsdGVkX1+tjML0WNR+cUj6cHMxVbPw05u7Vu9bGYc=
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id %any
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec logging log-types any log-level 1
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type initiate
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER install-vips interface dum0
set vpn ipsec site-to-site peer PEER remote-address 80.0.0.1
set vpn ipsec site-to-site peer PEER tunnel 1 install-routes main
set vpn ipsec site-to-site peer PEER tunnel 1 remote prefix 10.1.0.0/24
Step 4: Ping the IP address 80.0.0.1 from DUT1:
admin@DUT1$ ping 80.0.0.1 count 1 size 56 timeout 1Show output
PING 80.0.0.1 (80.0.0.1) 56(84) bytes of data.
64 bytes from 80.0.0.1: icmp_seq=1 ttl=64 time=0.740 ms

--- 80.0.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.740/0.740/0.740/0.000 ms
Step 5: Ping the IP address 80.0.0.2 from DUT0:
admin@DUT0$ ping 80.0.0.2 count 1 size 56 timeout 1Show output
PING 80.0.0.2 (80.0.0.2) 56(84) bytes of data.
64 bytes from 80.0.0.2: icmp_seq=1 ttl=64 time=0.454 ms

--- 80.0.0.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.454/0.454/0.454/0.000 ms
Step 6: Ping the IP address 10.1.0.2 from DUT0:
admin@DUT0$ ping 10.1.0.2 count 1 size 56 timeout 1Show output
PING 10.1.0.2 (10.1.0.2) 56(84) bytes of data.
64 bytes from 10.1.0.2: icmp_seq=1 ttl=64 time=2.06 ms

--- 10.1.0.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 2.056/2.056/2.056/0.000 ms
Step 7: Run the command interfaces dummy dum0 show on DUT1 and expect the following output:
Show output
-----------------------------------------------------------------
Name           IP Address           Admin  Oper  Vrf  Description
-----------------------------------------------------------------
dum0  10.3.0.1/32                   up     up
      fe80::8846:d9ff:fed4:52d4/64
Step 8: Ping the IP address 10.1.0.1 from DUT1:
admin@DUT1$ ping 10.1.0.1 local-address 10.3.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.3.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.592 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.592/0.592/0.592/0.000 ms
Step 9: Ping the IP address 10.1.0.2 from DUT1:
admin@DUT1$ ping 10.1.0.2 local-address 10.3.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.2 (10.1.0.2) from 10.3.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.2: icmp_seq=1 ttl=63 time=0.850 ms

--- 10.1.0.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.850/0.850/0.850/0.000 ms
Step 10: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
[1-9]\d? packetsShow output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, 80afc76b39ab7b4e_i a6e724ab7a94bfb6_r*
local  '80.0.0.1' @ 80.0.0.1[4500]
remote '80.0.0.2' @ 80.0.0.2[4500] [10.3.0.1]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 1s ago, rekeying in 13588s
peer-PEER-tunnel-VTI: #1, reqid 1, INSTALLED, TUNNEL-in-UDP, ESP:AES_GCM_16-256
installed 1s ago, rekeying in 3346s, expires in 3959s
in  c38d46d0 (0x90000000),    168 bytes,     2 packets,     0s ago
out c2bd5236 (0x90000000),    168 bytes,     2 packets,     0s ago
local  10.1.0.0/24
remote 10.3.0.1/32
Test VPN Roadwarrior Connection With Global Policies And VIPs Pool
Description
In this scenario, DUT0 uses global VPN
policies (or selectors) to encapsulate traffic.
DUT1 requests a virtual IP address from
DUT0 and it installed in dum0. Routes are
also automatically installed taking into
account the negotiated selectors.
Scenario
Step 1: Set the following configuration in DUT2 :
set interfaces ethernet eth1 address 10.1.0.2/24
set protocols static route 0.0.0.0/0 next-hop 10.1.0.1
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
Step 2: Set the following configuration in DUT0 :
set interfaces ethernet eth0 address 80.0.0.1/24
set interfaces ethernet eth1 address 10.1.0.1/24
set interfaces vti vti0 ipsec PEER
set interfaces vti vti0 local-address 80.0.0.1
set interfaces vti vti0 remote-address 0.0.0.0
set protocols static route 10.3.0.0/24 interface vti0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk %any encrypted-secret U2FsdGVkX19kcMSGULQY9WaCrYvWF0TnLwV/OTPl2Rs=
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id %any
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec pool POOL prefix 10.3.0.0/24
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type respond
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER local-address 80.0.0.1
set vpn ipsec site-to-site peer PEER pool POOL
set vpn ipsec site-to-site peer PEER vti local prefix 10.1.0.0/24
Step 3: Set the following configuration in DUT1 :
set interfaces dummy dum0
set interfaces ethernet eth0 address 80.0.0.2/24
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set system vrf main
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk %any encrypted-secret U2FsdGVkX19q/wr9B7QBig8zfBJ4f5bKXQtB9nOeogs=
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id %any
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec logging log-types any log-level 1
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type initiate
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER install-vips interface dum0
set vpn ipsec site-to-site peer PEER remote-address 80.0.0.1
set vpn ipsec site-to-site peer PEER tunnel 1 install-routes main
set vpn ipsec site-to-site peer PEER tunnel 1 remote prefix 10.1.0.0/24
Step 4: Ping the IP address 80.0.0.1 from DUT1:
admin@DUT1$ ping 80.0.0.1 count 1 size 56 timeout 1Show output
PING 80.0.0.1 (80.0.0.1) 56(84) bytes of data.
64 bytes from 80.0.0.1: icmp_seq=1 ttl=64 time=0.556 ms

--- 80.0.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.556/0.556/0.556/0.000 ms
Step 5: Ping the IP address 80.0.0.2 from DUT0:
admin@DUT0$ ping 80.0.0.2 count 1 size 56 timeout 1Show output
PING 80.0.0.2 (80.0.0.2) 56(84) bytes of data.
64 bytes from 80.0.0.2: icmp_seq=1 ttl=64 time=0.539 ms

--- 80.0.0.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.539/0.539/0.539/0.000 ms
Step 6: Ping the IP address 10.1.0.2 from DUT0:
admin@DUT0$ ping 10.1.0.2 count 1 size 56 timeout 1Show output
PING 10.1.0.2 (10.1.0.2) 56(84) bytes of data.
64 bytes from 10.1.0.2: icmp_seq=1 ttl=64 time=0.666 ms

--- 10.1.0.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.666/0.666/0.666/0.000 ms
Step 7: Run the command interfaces dummy dum0 show on DUT1 and expect the following output:
Show output
-----------------------------------------------------------------
Name           IP Address           Admin  Oper  Vrf  Description
-----------------------------------------------------------------
dum0  10.3.0.1/32                   up     up
      fe80::1809:29ff:fef8:d13e/64
Step 8: Ping the IP address 10.1.0.1 from DUT1:
admin@DUT1$ ping 10.1.0.1 local-address 10.3.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.3.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.864 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.864/0.864/0.864/0.000 ms
Step 9: Ping the IP address 10.1.0.2 from DUT1:
admin@DUT1$ ping 10.1.0.2 local-address 10.3.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.2 (10.1.0.2) from 10.3.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.2: icmp_seq=1 ttl=63 time=1.49 ms

--- 10.1.0.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 1.494/1.494/1.494/0.000 ms
Step 10: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
[1-9]\d? packetsShow output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, d61dfe61202979a3_i 60cc8c214dc89a49_r*
local  '80.0.0.1' @ 80.0.0.1[4500]
remote '80.0.0.2' @ 80.0.0.2[4500] [10.3.0.1]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 1s ago, rekeying in 17429s
peer-PEER-tunnel-VTI: #1, reqid 1, INSTALLED, TUNNEL-in-UDP, ESP:AES_GCM_16-256
installed 1s ago, rekeying in 3290s, expires in 3959s
in  c30dfd05 (0x90000000),    168 bytes,     2 packets,     0s ago
out c21915ed (0x90000000),    168 bytes,     2 packets,     0s ago
local  10.1.0.0/24
remote 10.3.0.1/32