Duplicate
The following scenarios demonstrate how to configure port
mirroring using the traffic policy duplicate feature.
Port mirroring duplicates network packets and forwards copies
to monitoring destinations while preserving the original traffic flow.
traffic selectors can be used to filter which packets
should be duplicated based on protocol, addresses, or other criteria.
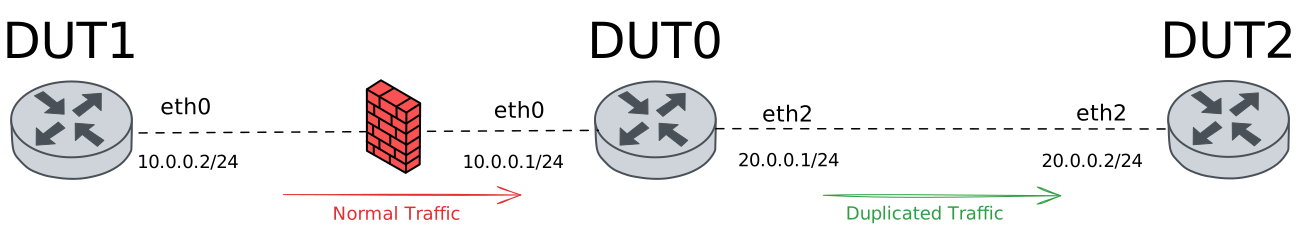
Test duplicate local traffic to an interface
Description
This scenario configures link-level port mirroring on DUT0’s (‘eth0’ interface). Both ingress (link-in) and egress (link-out) traffic policies are applied to duplicate all traffic to another physical interface.
Scenario
Step 1: Set the following configuration in DUT0 :
set interfaces ethernet eth0 address 10.0.0.1/24
set interfaces ethernet eth0 traffic policy link-in DUP_POLICY
set interfaces ethernet eth0 traffic policy link-out DUP_POLICY
set interfaces ethernet eth2 address 20.0.0.1/24
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set traffic policy DUP_POLICY rule 1 action accept
set traffic policy DUP_POLICY rule 1 duplicate device eth2
Step 2: Set the following configuration in DUT1 :
set interfaces ethernet eth0 address 10.0.0.2/24
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
Step 3: Set the following configuration in DUT2 :
set interfaces ethernet eth2 address 20.0.0.2/24
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
Step 4: Ping the IP address 10.0.0.1 from DUT1:
admin@DUT1$ ping 10.0.0.1 count 1 size 56 timeout 1Show output
PING 10.0.0.1 (10.0.0.1) 56(84) bytes of data.
64 bytes from 10.0.0.1: icmp_seq=1 ttl=64 time=0.623 ms

--- 10.0.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.623/0.623/0.623/0.000 ms
Step 5: Ping the IP address 20.0.0.1 from DUT2:
admin@DUT2$ ping 20.0.0.1 count 1 size 56 timeout 1Show output
PING 20.0.0.1 (20.0.0.1) 56(84) bytes of data.
64 bytes from 20.0.0.1: icmp_seq=1 ttl=64 time=0.535 ms

--- 20.0.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.535/0.535/0.535/0.000 ms
Step 6: Modify the following configuration lines in DUT0 :
set service echo port 5050
Note
Start packet capture on DUT0 eth2 to monitor duplicated traffic
Step 7: Run the command monitor test connection client 10.0.0.1 5050 udp on DUT1.
Note
Now it is important to generate some traffic from DUT1 to DUT0 echo service.
Note
Stop packet capture. Expected output:
Show output
tcpdump: verbose output suppressed, use -v[v]... for full protocol decode
listening on eth2, link-type EN10MB (Ethernet), snapshot length 262144 bytes
18:36:08.529388 IP 10.0.0.2.54789 > 10.0.0.1.5050: UDP, length 17
18:36:08.530437 IP 10.0.0.1.5050 > 10.0.0.2.54789: UDP, length 17
18:36:09.530813 IP 10.0.0.2.54789 > 10.0.0.1.5050: UDP, length 17
18:36:09.531936 IP 10.0.0.1.5050 > 10.0.0.2.54789: UDP, length 17
18:36:10.532525 IP 10.0.0.2.54789 > 10.0.0.1.5050: UDP, length 17
18:36:10.533533 IP 10.0.0.1.5050 > 10.0.0.2.54789: UDP, length 17
18:36:11.536679 IP 10.0.0.2.54789 > 10.0.0.1.5050: UDP, length 17
18:36:11.539635 IP 10.0.0.1.5050 > 10.0.0.2.54789: UDP, length 17
18:36:11.977785 ARP, Request who-has 20.0.0.2 tell 20.0.0.1, length 28
18:36:11.977794 ARP, Request who-has 10.0.0.2 tell 10.0.0.1, length 28
18:36:11.977993 ARP, Reply 10.0.0.2 is-at de:ad:be:ef:6c:10, length 28
18:36:11.978025 ARP, Reply 20.0.0.2 is-at de:ad:be:ef:6c:22, length 28
18:36:12.537636 IP 10.0.0.2.54789 > 10.0.0.1.5050: UDP, length 17
18:36:12.538688 IP 10.0.0.1.5050 > 10.0.0.2.54789: UDP, length 17
^C

14 packets captured
14 packets received by filter
0 packets dropped by kernel
admin@osdx$
Test duplicate local traffic to a remote IP
Description
This scenario configures remote port mirroring on DUT0 (‘eth0’ interface). Local-in and local-out traffic policies duplicate traffic to a remote IP address. A traffic selector is configured to filter and duplicate only UDP traffic.
Scenario
Step 1: Set the following configuration in DUT0 :
set interfaces ethernet eth0 address 10.0.0.1/24
set interfaces ethernet eth0 traffic policy local-in DUP_POLICY
set interfaces ethernet eth0 traffic policy local-out DUP_POLICY
set interfaces ethernet eth2 address 20.0.0.1/24
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set traffic policy DUP_POLICY rule 1 action accept
set traffic policy DUP_POLICY rule 1 duplicate remote 20.0.0.2
set traffic policy DUP_POLICY rule 1 selector UDP_SEL
set traffic selector UDP_SEL rule 1 protocol udp
Step 2: Set the following configuration in DUT1 :
set interfaces ethernet eth0 address 10.0.0.2/24
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
Step 3: Set the following configuration in DUT2 :
set interfaces ethernet eth2 address 20.0.0.2/24
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
Step 4: Ping the IP address 10.0.0.1 from DUT1:
admin@DUT1$ ping 10.0.0.1 count 1 size 56 timeout 1Show output
PING 10.0.0.1 (10.0.0.1) 56(84) bytes of data.
64 bytes from 10.0.0.1: icmp_seq=1 ttl=64 time=0.842 ms

--- 10.0.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.842/0.842/0.842/0.000 ms
Step 5: Ping the IP address 20.0.0.1 from DUT2:
admin@DUT2$ ping 20.0.0.1 count 1 size 56 timeout 1Show output
PING 20.0.0.1 (20.0.0.1) 56(84) bytes of data.
64 bytes from 20.0.0.1: icmp_seq=1 ttl=64 time=0.776 ms

--- 20.0.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.776/0.776/0.776/0.000 ms
Note
Start packet capture on DUT2 eth2 to monitor duplicated traffic
Step 6: Initiate a tcp connection from DUT1 to DUT0 and exchange messages between both endpoints
admin@DUT0$ monitor test connection server 5050 tcp
admin@DUT1$ monitor test connection client 10.0.0.1 5050 tcp
Step 7: Initiate a udp connection from DUT1 to DUT0 and exchange messages between both endpoints
admin@DUT0$ monitor test connection server 5050 udp
admin@DUT1$ monitor test connection client 10.0.0.1 5050 udp
Note
Stop packet capture. Expected output:
Show output
tcpdump: verbose output suppressed, use -v[v]... for full protocol decode
listening on eth2, link-type EN10MB (Ethernet), snapshot length 262144 bytes
18:36:23.176221 IP6 :: > ff02::1:ffef:6c22: ICMP6, neighbor solicitation, who has fe80::dcad:beff:feef:6c22, length 32
18:36:24.200239 IP6 fe80::dcad:beff:feef:6c22 > ff02::16: HBH ICMP6, multicast listener report v2, 4 group record(s), length 88
18:36:24.212198 IP6 fe80::dcad:beff:feef:6c22 > ff02::16: HBH ICMP6, multicast listener report v2, 1 group record(s), length 28
18:36:24.324215 IP6 fe80::dcad:beff:feef:6c22 > ff02::16: HBH ICMP6, multicast listener report v2, 4 group record(s), length 88
18:36:25.000239 IP6 fe80::dcad:beff:feef:6c22 > ff02::16: HBH ICMP6, multicast listener report v2, 1 group record(s), length 28
18:36:27.641303 IP 10.0.0.2.45740 > 10.0.0.1.5050: UDP, length 20
18:36:27.676633 IP 10.0.0.1.5050 > 10.0.0.2.45740: UDP, length 20
18:36:27.707090 IP 10.0.0.2.45740 > 10.0.0.1.5050: UDP, length 20
18:36:27.749317 IP 10.0.0.1.5050 > 10.0.0.2.45740: UDP, length 20
18:36:27.794001 IP 10.0.0.2.45740 > 10.0.0.1.5050: UDP, length 20
18:36:27.825702 IP 10.0.0.1.5050 > 10.0.0.2.45740: UDP, length 20
18:36:27.878443 IP 10.0.0.2.45740 > 10.0.0.1.5050: UDP, length 20
18:36:27.932561 IP 10.0.0.1.5050 > 10.0.0.2.45740: UDP, length 20
18:36:27.986629 IP 10.0.0.2.45740 > 10.0.0.1.5050: UDP, length 20
18:36:28.029841 IP 10.0.0.1.5050 > 10.0.0.2.45740: UDP, length 20
18:36:28.103895 ARP, Request who-has 20.0.0.2 tell 20.0.0.1, length 28
18:36:28.103911 ARP, Reply 20.0.0.2 is-at de:ad:be:ef:6c:22, length 28
^C

17 packets captured
17 packets received by filter
0 packets dropped by kernel
admin@osdx$
Note
Note that only UDP traffic is captured because the traffic selector is configured to filter UDP packets exclusively.
Test duplicate local traffic to a remote IP with VRF
Description
This scenario configures remote port mirroring on DUT0 (‘eth0’ interface). Local-in and local-out traffic policies duplicate traffic to a remote IP address. The interface is configured within a VRF, which must be specified as the output VRF. A traffic selector is configured to filter and duplicate only UDP traffic.
Scenario
Step 1: Set the following configuration in DUT0 :
set interfaces ethernet eth0 address 10.0.0.1/24
set interfaces ethernet eth0 traffic policy local-in DUP_POLICY
set interfaces ethernet eth0 traffic policy local-out DUP_POLICY
set interfaces ethernet eth2 address 20.0.0.1/24
set interfaces ethernet eth2 vrf VRF1
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set system vrf VRF1
set traffic policy DUP_POLICY rule 1 action accept
set traffic policy DUP_POLICY rule 1 duplicate remote 20.0.0.2 local-vrf VRF1
set traffic policy DUP_POLICY rule 1 selector UDP_SEL
set traffic selector UDP_SEL rule 1 protocol udp
Step 2: Set the following configuration in DUT1 :
set interfaces ethernet eth0 address 10.0.0.2/24
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
Step 3: Set the following configuration in DUT2 :
set interfaces ethernet eth2 address 20.0.0.2/24
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
Step 4: Ping the IP address 10.0.0.1 from DUT1:
admin@DUT1$ ping 10.0.0.1 count 1 size 56 timeout 1Show output
PING 10.0.0.1 (10.0.0.1) 56(84) bytes of data.
64 bytes from 10.0.0.1: icmp_seq=1 ttl=64 time=0.683 ms

--- 10.0.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.683/0.683/0.683/0.000 ms
Step 5: Ping the IP address 20.0.0.1 from DUT2:
admin@DUT2$ ping 20.0.0.1 count 1 size 56 timeout 1Show output
PING 20.0.0.1 (20.0.0.1) 56(84) bytes of data.
64 bytes from 20.0.0.1: icmp_seq=1 ttl=64 time=0.593 ms

--- 20.0.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.593/0.593/0.593/0.000 ms
Note
Start packet capture on DUT2 eth2 to monitor duplicated traffic
Step 6: Initiate a tcp connection from DUT1 to DUT0 and exchange messages between both endpoints
admin@DUT0$ monitor test connection server 5050 tcp
admin@DUT1$ monitor test connection client 10.0.0.1 5050 tcp
Step 7: Initiate a udp connection from DUT1 to DUT0 and exchange messages between both endpoints
admin@DUT0$ monitor test connection server 5050 udp
admin@DUT1$ monitor test connection client 10.0.0.1 5050 udp
Note
Stop packet capture. Expected output:
Show output
tcpdump: verbose output suppressed, use -v[v]... for full protocol decode
listening on eth2, link-type EN10MB (Ethernet), snapshot length 262144 bytes
18:36:38.699112 IP6 :: > ff02::16: HBH ICMP6, multicast listener report v2, 3 group record(s), length 68
18:36:38.731106 IP6 :: > ff02::1:ffef:6c22: ICMP6, neighbor solicitation, who has fe80::dcad:beff:feef:6c22, length 32
18:36:39.755140 IP6 fe80::dcad:beff:feef:6c22 > ff02::16: HBH ICMP6, multicast listener report v2, 4 group record(s), length 88
18:36:39.767101 IP6 fe80::dcad:beff:feef:6c22 > ff02::16: HBH ICMP6, multicast listener report v2, 1 group record(s), length 28
18:36:40.267109 IP6 fe80::dcad:beff:feef:6c22 > ff02::16: HBH ICMP6, multicast listener report v2, 1 group record(s), length 28
18:36:40.555111 IP6 fe80::dcad:beff:feef:6c22 > ff02::16: HBH ICMP6, multicast listener report v2, 4 group record(s), length 88
18:36:43.130117 IP 10.0.0.2.44649 > 10.0.0.1.5050: UDP, length 20
18:36:43.157083 IP 10.0.0.1.5050 > 10.0.0.2.44649: UDP, length 20
18:36:43.183392 IP 10.0.0.2.44649 > 10.0.0.1.5050: UDP, length 20
18:36:43.211247 IP 10.0.0.1.5050 > 10.0.0.2.44649: UDP, length 20
18:36:43.239377 IP 10.0.0.2.44649 > 10.0.0.1.5050: UDP, length 20
18:36:43.267061 IP 10.0.0.1.5050 > 10.0.0.2.44649: UDP, length 20
18:36:43.299351 IP 10.0.0.2.44649 > 10.0.0.1.5050: UDP, length 20
18:36:43.325568 IP 10.0.0.1.5050 > 10.0.0.2.44649: UDP, length 20
18:36:43.363821 IP 10.0.0.2.44649 > 10.0.0.1.5050: UDP, length 20
18:36:43.390533 IP 10.0.0.1.5050 > 10.0.0.2.44649: UDP, length 20
18:36:43.530795 ARP, Request who-has 20.0.0.2 tell 20.0.0.1, length 28
18:36:43.530808 ARP, Reply 20.0.0.2 is-at de:ad:be:ef:6c:22, length 28
^C

18 packets captured
18 packets received by filter
0 packets dropped by kernel
admin@osdx$
Note
Note that only UDP traffic is captured because the traffic selector is configured to filter UDP packets exclusively.