Ppk
This set of tests shows how to configure and connect more than two subnets with each other through a VPN tunnel using PPK authentication in different ways.
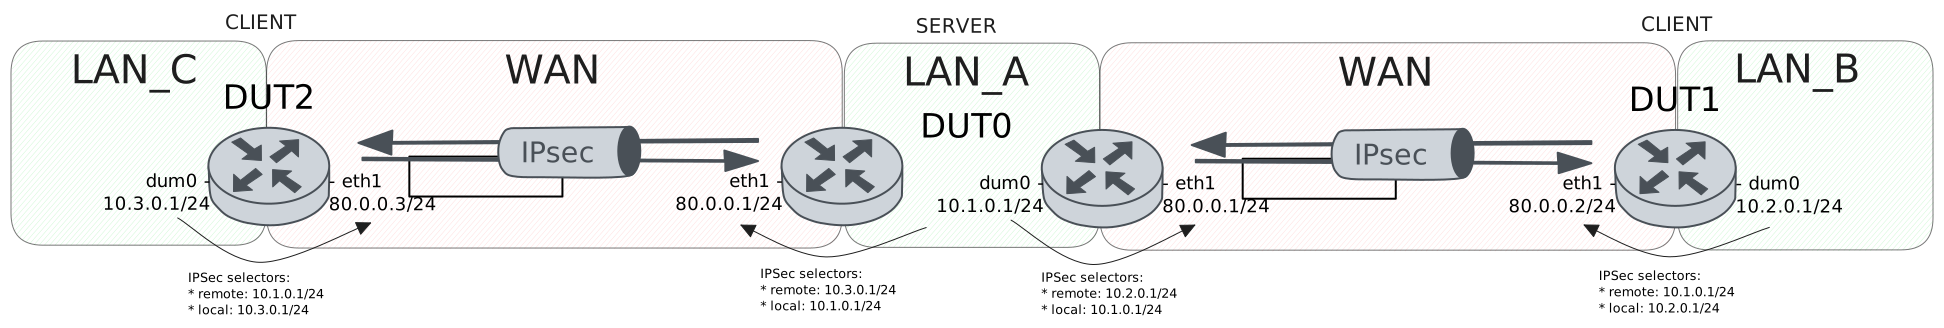
Test PPK Options
Description
In this test, we will check the different options for PPK authentication (i.e., when it is required or not, when it remains unmatched, etc.).
Scenario
Note
Set default configuration for both DUTs, where PPK is not required and the PPK is the same.
Step 1: Set the following configuration in DUT0 :
set interfaces dummy dum0 address 10.1.0.1/24
set interfaces ethernet eth1 address 80.0.0.1/24
set protocols static route 10.2.0.0/24 interface dum0
set protocols static route 10.3.0.0/24 interface dum0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets eap carol encrypted-secret U2FsdGVkX19zQ1QF4wY52SgNfGwftdtaaT9qvW0sdjo=
set vpn ipsec auth-profile AUTH-SA global-secrets eap dave encrypted-secret U2FsdGVkX1+At9cWd6r792MtmrfjoFapV+/AOiX5e0E=
set vpn ipsec auth-profile AUTH-SA global-secrets ppk carol@teldat.org file 'running://ppk_carol.key'
set vpn ipsec auth-profile AUTH-SA global-secrets ppk dave@teldat.org file 'running://ppk_dave.key'
set vpn ipsec auth-profile AUTH-SA local ca-cert-file 'running://ca.crt'
set vpn ipsec auth-profile AUTH-SA local cert-file 'running://server.crt'
set vpn ipsec auth-profile AUTH-SA local id CN=moon.teldat.org
set vpn ipsec auth-profile AUTH-SA local key file 'running://server.priv.pem'
set vpn ipsec auth-profile AUTH-SA mirror-config false
set vpn ipsec auth-profile AUTH-SA remote auth eap %any type ttls
set vpn ipsec auth-profile AUTH-SA remote ppk id '*@teldat.org'
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec logging log-types any log-level 1
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type respond
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER local-address 80.0.0.1
set vpn ipsec site-to-site peer PEER tunnel 1 local prefix 10.1.0.0/24
set vpn ipsec site-to-site peer PEER tunnel 1 local-interface dum0
Step 2: Set the following configuration in DUT1 :
set interfaces dummy dum0 address 10.2.0.1/24
set interfaces ethernet eth1 address 80.0.0.2/24
set protocols static route 10.1.0.0/24 interface dum0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets eap carol encrypted-secret U2FsdGVkX18Eg2g1uDa3BaGk5YrQMbNM2neoL1u9/6g=
set vpn ipsec auth-profile AUTH-SA global-secrets ppk carol@teldat.org file 'running://ppk_carol.key'
set vpn ipsec auth-profile AUTH-SA local auth eap carol type ttls
set vpn ipsec auth-profile AUTH-SA local id carol
set vpn ipsec auth-profile AUTH-SA local ppk id carol@teldat.org
set vpn ipsec auth-profile AUTH-SA mirror-config false
set vpn ipsec auth-profile AUTH-SA remote ca-cert-file 'running://ca.crt'
set vpn ipsec auth-profile AUTH-SA remote id CN=moon.teldat.org
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec logging log-types any log-level 1
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type initiate
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER local-address 80.0.0.2
set vpn ipsec site-to-site peer PEER remote-address 80.0.0.1
set vpn ipsec site-to-site peer PEER tunnel 1 local prefix 10.2.0.0/24
set vpn ipsec site-to-site peer PEER tunnel 1 local-interface dum0
set vpn ipsec site-to-site peer PEER tunnel 1 remote prefix 10.1.0.0/24
Step 3: Ping the IP address 80.0.0.2 from DUT1:
admin@DUT1$ ping 80.0.0.2 count 1 size 56 timeout 1Show output
PING 80.0.0.2 (80.0.0.2) 56(84) bytes of data.
64 bytes from 80.0.0.2: icmp_seq=1 ttl=64 time=0.032 ms

--- 80.0.0.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.032/0.032/0.032/0.000 ms
Step 4: Ping the IP address 80.0.0.1 from DUT0:
admin@DUT0$ ping 80.0.0.1 count 1 size 56 timeout 1Show output
PING 80.0.0.1 (80.0.0.1) 56(84) bytes of data.
64 bytes from 80.0.0.1: icmp_seq=1 ttl=64 time=0.447 ms

--- 80.0.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.447/0.447/0.447/0.000 ms
Step 5: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256\/PPK.*\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*remote\s+10.2.0.*Show output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, 25aa4a9dcfeabb95_i 3eb3c5a9a2d1374b_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'carol' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 0s ago, rekeying in 13218s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 0s ago, rekeying in 3376s, expires in 3960s
in  c29ba11d,      0 bytes,     0 packets
out cf49cdda,      0 bytes,     0 packets
local  10.1.0.0/24
remote 10.2.0.0/24
Step 6: Ping the IP address 10.2.0.1 from DUT0:
admin@DUT0$ ping 10.2.0.1 local-address 10.1.0.1 count 1 size 56 timeout 1Show output
PING 10.2.0.1 (10.2.0.1) from 10.1.0.1 : 56(84) bytes of data.
64 bytes from 10.2.0.1: icmp_seq=1 ttl=64 time=0.443 ms

--- 10.2.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.443/0.443/0.443/0.000 ms
Step 7: Ping the IP address 10.1.0.1 from DUT1:
admin@DUT1$ ping 10.1.0.1 local-address 10.2.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.2.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.372 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.372/0.372/0.372/0.000 ms
Step 8: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256\/PPK.*\s+.*\s+.*\s+.*\s+.*[1-9]\d? packets.*\s+.*[1-9]\d? packets.*\s+.*\s+.*remote\s+10.2.0.*Show output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, 25aa4a9dcfeabb95_i 3eb3c5a9a2d1374b_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'carol' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 1s ago, rekeying in 13217s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 1s ago, rekeying in 3375s, expires in 3959s
in  c29ba11d,    168 bytes,     2 packets,     0s ago
out cf49cdda,    168 bytes,     2 packets,     0s ago
local  10.1.0.0/24
remote 10.2.0.0/24
Note
Delete the PPK from DUT0 and check that the SA falls back to standard authentication.
Step 9: Modify the following configuration lines in DUT0 :
delete vpn ipsec auth-profile AUTH-SA global-secrets ppk carol@teldat.org
Step 10: Run the command vpn ipsec clear peer PEER on DUT0 and expect the following output:
Show output
Tunnels cleared for peer PEER
Step 11: Run the command vpn ipsec clear peer PEER on DUT1 and expect the following output:
Show output
Tunnels cleared for peer PEER
Step 12: Run the command vpn ipsec initiate peer PEER on DUT1 and expect the following output:
Show output
Initiated tunnels: 1
Step 13: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256.*\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*remote\s+10.2.0.*Show output
vpn-peer-PEER: #3, ESTABLISHED, IKEv2, ddfd8e03922dcdc5_i 4385374e9be4b1d6_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'carol' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 0s ago, rekeying in 20812s
peer-PEER-tunnel-1: #3, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 0s ago, rekeying in 3452s, expires in 3960s
in  c2529242,      0 bytes,     0 packets
out c3fcb5c3,      0 bytes,     0 packets
local  10.1.0.0/24
remote 10.2.0.0/24
Step 14: Ping the IP address 10.2.0.1 from DUT0:
admin@DUT0$ ping 10.2.0.1 local-address 10.1.0.1 count 1 size 56 timeout 1Show output
PING 10.2.0.1 (10.2.0.1) from 10.1.0.1 : 56(84) bytes of data.
64 bytes from 10.2.0.1: icmp_seq=1 ttl=64 time=8.30 ms

--- 10.2.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 8.297/8.297/8.297/0.000 ms
Step 15: Ping the IP address 10.1.0.1 from DUT1:
admin@DUT1$ ping 10.1.0.1 local-address 10.2.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.2.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.761 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.761/0.761/0.761/0.000 ms
Step 16: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256.*\s+.*\s+.*\s+.*\s+.*[1-9]\d? packets.*\s+.*[1-9]\d? packets.*\s+.*\s+.*remote\s+10.2.0.*Show output
vpn-peer-PEER: #3, ESTABLISHED, IKEv2, ddfd8e03922dcdc5_i 4385374e9be4b1d6_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'carol' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256
established 0s ago, rekeying in 20812s
peer-PEER-tunnel-1: #3, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 0s ago, rekeying in 3452s, expires in 3960s
in  c2529242,    168 bytes,     2 packets,     0s ago
out c3fcb5c3,    168 bytes,     2 packets,     0s ago
local  10.1.0.0/24
remote 10.2.0.0/24
Note
Set the PPK as required in DUT0 and, with DUT1’s corresponding PPK deleted, check that the connection fails.
Step 17: Modify the following configuration lines in DUT0 :
set vpn ipsec auth-profile AUTH-SA remote ppk required
Step 18: Run the command vpn ipsec clear peer PEER on DUT0 and expect the following output:
Show output
Tunnels cleared for peer PEER
Step 19: Run the command vpn ipsec clear peer PEER on DUT1 and expect the following output:
Show output
No established tunnels for peer PEER
Step 20: Run the command vpn ipsec initiate peer PEER on DUT1 and expect the following output:
Show output
Initiated tunnels: 0
Step 21: Expect a failure in the following command:
Ping the IP address 10.2.0.1 from DUT0:
admin@DUT0$ ping 10.2.0.1 local-address 10.1.0.1 count 1 size 56 timeout 1Show output
PING 10.2.0.1 (10.2.0.1) from 10.1.0.1 : 56(84) bytes of data.

--- 10.2.0.1 ping statistics ---
1 packets transmitted, 0 received, 100% packet loss, time 0ms
Note
Set the PPK as required in DUT1 and change the PPK in DUT0 back to not required. Check that the connection is still failing.
Step 22: Modify the following configuration lines in DUT0 :
delete vpn ipsec auth-profile AUTH-SA remote ppk required
Step 23: Modify the following configuration lines in DUT1 :
set vpn ipsec auth-profile AUTH-SA local ppk required
Step 24: Run the command vpn ipsec clear peer PEER on DUT0 and expect the following output:
Show output
No established tunnels for peer PEER
Step 25: Run the command vpn ipsec clear peer PEER on DUT1 and expect the following output:
Show output
No established tunnels for peer PEER
Step 26: Run the command vpn ipsec initiate peer PEER on DUT1 and expect the following output:
Show output
Initiated tunnels: 0
Step 27: Expect a failure in the following command:
Ping the IP address 10.2.0.1 from DUT0:
admin@DUT0$ ping 10.2.0.1 local-address 10.1.0.1 count 1 size 56 timeout 1Show output
PING 10.2.0.1 (10.2.0.1) from 10.1.0.1 : 56(84) bytes of data.

--- 10.2.0.1 ping statistics ---
1 packets transmitted, 0 received, 100% packet loss, time 0ms
Test PPK EAP-TTLS STS
Description
Test the site-to-site VPN with PPK authentication and EAP-TTLS
Scenario
Step 1: Set the following configuration in DUT0 :
set interfaces dummy dum0 address 10.1.0.1/24
set interfaces ethernet eth1 address 80.0.0.1/24
set protocols static route 10.2.0.0/24 interface dum0
set protocols static route 10.3.0.0/24 interface dum0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets eap carol encrypted-secret U2FsdGVkX1+AdMAtn3yagUQJestA9RAnKrKt6FG28Fc=
set vpn ipsec auth-profile AUTH-SA global-secrets eap dave encrypted-secret U2FsdGVkX1/mBmQnx3vxcAQkIZwi828DwnN1XjeCJr0=
set vpn ipsec auth-profile AUTH-SA global-secrets ppk carol@teldat.org file 'running://ppk_carol.key'
set vpn ipsec auth-profile AUTH-SA global-secrets ppk dave@teldat.org file 'running://ppk_dave.key'
set vpn ipsec auth-profile AUTH-SA local ca-cert-file 'running://ca.crt'
set vpn ipsec auth-profile AUTH-SA local cert-file 'running://server.crt'
set vpn ipsec auth-profile AUTH-SA local id CN=moon.teldat.org
set vpn ipsec auth-profile AUTH-SA local key file 'running://server.priv.pem'
set vpn ipsec auth-profile AUTH-SA mirror-config false
set vpn ipsec auth-profile AUTH-SA remote auth eap %any type ttls
set vpn ipsec auth-profile AUTH-SA remote ppk id '*@teldat.org'
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec logging log-types any log-level 1
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type respond
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER local-address 80.0.0.1
set vpn ipsec site-to-site peer PEER tunnel 1 local prefix 10.1.0.0/24
set vpn ipsec site-to-site peer PEER tunnel 1 local-interface dum0
Step 2: Set the following configuration in DUT1 :
set interfaces dummy dum0 address 10.2.0.1/24
set interfaces ethernet eth1 address 80.0.0.2/24
set protocols static route 10.1.0.0/24 interface dum0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets eap carol encrypted-secret U2FsdGVkX186cN1vpxOLttW0lDbJCXq79XvfAVS4TX4=
set vpn ipsec auth-profile AUTH-SA global-secrets ppk carol@teldat.org file 'running://ppk_carol.key'
set vpn ipsec auth-profile AUTH-SA local auth eap carol type ttls
set vpn ipsec auth-profile AUTH-SA local id carol
set vpn ipsec auth-profile AUTH-SA local ppk id carol@teldat.org
set vpn ipsec auth-profile AUTH-SA mirror-config false
set vpn ipsec auth-profile AUTH-SA remote ca-cert-file 'running://ca.crt'
set vpn ipsec auth-profile AUTH-SA remote id CN=moon.teldat.org
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec logging log-types any log-level 1
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type initiate
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER local-address 80.0.0.2
set vpn ipsec site-to-site peer PEER remote-address 80.0.0.1
set vpn ipsec site-to-site peer PEER tunnel 1 local prefix 10.2.0.0/24
set vpn ipsec site-to-site peer PEER tunnel 1 local-interface dum0
set vpn ipsec site-to-site peer PEER tunnel 1 remote prefix 10.1.0.0/24
Step 3: Ping the IP address 80.0.0.2 from DUT1:
admin@DUT1$ ping 80.0.0.2 count 1 size 56 timeout 1Show output
PING 80.0.0.2 (80.0.0.2) 56(84) bytes of data.
64 bytes from 80.0.0.2: icmp_seq=1 ttl=64 time=0.029 ms

--- 80.0.0.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.029/0.029/0.029/0.000 ms
Step 4: Ping the IP address 80.0.0.1 from DUT0:
admin@DUT0$ ping 80.0.0.1 count 1 size 56 timeout 1Show output
PING 80.0.0.1 (80.0.0.1) 56(84) bytes of data.
64 bytes from 80.0.0.1: icmp_seq=1 ttl=64 time=0.030 ms

--- 80.0.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.030/0.030/0.030/0.000 ms
Step 5: Set the following configuration in DUT2 :
set interfaces dummy dum0 address 10.3.0.1/24
set interfaces ethernet eth1 address 80.0.0.3/24
set protocols static route 0.0.0.0/0 interface dum0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets eap dave encrypted-secret U2FsdGVkX18DF1WNb6D93cUxG0IrE3YiD8SYe/Bg4UE=
set vpn ipsec auth-profile AUTH-SA global-secrets ppk dave@teldat.org file 'running://ppk_dave.key'
set vpn ipsec auth-profile AUTH-SA local auth eap dave type ttls
set vpn ipsec auth-profile AUTH-SA local id dave
set vpn ipsec auth-profile AUTH-SA local ppk id dave@teldat.org
set vpn ipsec auth-profile AUTH-SA mirror-config false
set vpn ipsec auth-profile AUTH-SA remote ca-cert-file 'running://ca.crt'
set vpn ipsec auth-profile AUTH-SA remote id CN=moon.teldat.org
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec logging log-types any log-level 1
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type initiate
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER local-address 80.0.0.3
set vpn ipsec site-to-site peer PEER remote-address 80.0.0.1
set vpn ipsec site-to-site peer PEER tunnel 1 local prefix 10.3.0.0/24
set vpn ipsec site-to-site peer PEER tunnel 1 local-interface dum0
set vpn ipsec site-to-site peer PEER tunnel 1 remote prefix 10.1.0.0/24
Step 6: Ping the IP address 10.1.0.1 from DUT2:
admin@DUT2$ ping 10.1.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.415 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.415/0.415/0.415/0.000 ms
Step 7: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256\/PPK.*\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*remote\s+10.2.0.*Show output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, fece06b868c0bae9_i b028b2d5a3d900cd_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'carol' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 4s ago, rekeying in 18035s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 4s ago, rekeying in 3278s, expires in 3956s
in  c988bc82,      0 bytes,     0 packets
out c1372ee3,      0 bytes,     0 packets
local  10.1.0.0/24
remote 10.2.0.0/24
vpn-peer-PEER: #2, ESTABLISHED, IKEv2, 14432d403b72a0da_i 0197470f22b6cbdf_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'dave' @ 80.0.0.3[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 0s ago, rekeying in 20442s
peer-PEER-tunnel-1: #2, reqid 2, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 0s ago, rekeying in 3316s, expires in 3960s
in  c18e28b5,     84 bytes,     1 packets,     0s ago
out c53a8dba,     84 bytes,     1 packets,     0s ago
local  10.1.0.0/24
remote 10.3.0.0/24
Step 8: Ping the IP address 10.2.0.1 from DUT0:
admin@DUT0$ ping 10.2.0.1 local-address 10.1.0.1 count 1 size 56 timeout 1Show output
PING 10.2.0.1 (10.2.0.1) from 10.1.0.1 : 56(84) bytes of data.
64 bytes from 10.2.0.1: icmp_seq=1 ttl=64 time=0.412 ms

--- 10.2.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.412/0.412/0.412/0.000 ms
Step 9: Ping the IP address 10.1.0.1 from DUT1:
admin@DUT1$ ping 10.1.0.1 local-address 10.2.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.2.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.426 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.426/0.426/0.426/0.000 ms
Step 10: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256\/PPK.*\s+.*\s+.*\s+.*\s+.*[1-9]\d? packets.*\s+.*[1-9]\d? packets.*\s+.*\s+.*remote\s+10.2.0.*Show output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, fece06b868c0bae9_i b028b2d5a3d900cd_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'carol' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 5s ago, rekeying in 18034s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 5s ago, rekeying in 3277s, expires in 3955s
in  c988bc82,    168 bytes,     2 packets,     0s ago
out c1372ee3,    168 bytes,     2 packets,     0s ago
local  10.1.0.0/24
remote 10.2.0.0/24
vpn-peer-PEER: #2, ESTABLISHED, IKEv2, 14432d403b72a0da_i 0197470f22b6cbdf_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'dave' @ 80.0.0.3[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 1s ago, rekeying in 20441s
peer-PEER-tunnel-1: #2, reqid 2, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 1s ago, rekeying in 3315s, expires in 3959s
in  c18e28b5,     84 bytes,     1 packets,     1s ago
out c53a8dba,     84 bytes,     1 packets,     1s ago
local  10.1.0.0/24
remote 10.3.0.0/24
Step 11: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256\/PPK\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*remote\s+10.3.0.*Show output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, fece06b868c0bae9_i b028b2d5a3d900cd_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'carol' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 5s ago, rekeying in 18034s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 5s ago, rekeying in 3277s, expires in 3955s
in  c988bc82,    168 bytes,     2 packets,     0s ago
out c1372ee3,    168 bytes,     2 packets,     0s ago
local  10.1.0.0/24
remote 10.2.0.0/24
vpn-peer-PEER: #2, ESTABLISHED, IKEv2, 14432d403b72a0da_i 0197470f22b6cbdf_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'dave' @ 80.0.0.3[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 1s ago, rekeying in 20441s
peer-PEER-tunnel-1: #2, reqid 2, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 1s ago, rekeying in 3315s, expires in 3959s
in  c18e28b5,     84 bytes,     1 packets,     1s ago
out c53a8dba,     84 bytes,     1 packets,     1s ago
local  10.1.0.0/24
remote 10.3.0.0/24
Step 12: Ping the IP address 10.3.0.1 from DUT0:
admin@DUT0$ ping 10.3.0.1 local-address 10.1.0.1 count 1 size 56 timeout 1Show output
PING 10.3.0.1 (10.3.0.1) from 10.1.0.1 : 56(84) bytes of data.
64 bytes from 10.3.0.1: icmp_seq=1 ttl=64 time=0.448 ms

--- 10.3.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.448/0.448/0.448/0.000 ms
Step 13: Ping the IP address 10.1.0.1 from DUT2:
admin@DUT2$ ping 10.1.0.1 local-address 10.3.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.3.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.381 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.381/0.381/0.381/0.000 ms
Step 14: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256\/PPK\s+.*\s+.*\s+.*\s+.*[1-9]\d? packets.*\s+.*[1-9]\d? packets.*\s+.*\s+.*remote\s+10.3.0.*Show output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, fece06b868c0bae9_i b028b2d5a3d900cd_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'carol' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 12s ago, rekeying in 18027s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 12s ago, rekeying in 3270s, expires in 3948s
in  c988bc82,    168 bytes,     2 packets,     7s ago
out c1372ee3,    168 bytes,     2 packets,     7s ago
local  10.1.0.0/24
remote 10.2.0.0/24
vpn-peer-PEER: #2, ESTABLISHED, IKEv2, 14432d403b72a0da_i 0197470f22b6cbdf_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'dave' @ 80.0.0.3[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 8s ago, rekeying in 20434s
peer-PEER-tunnel-1: #2, reqid 2, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 8s ago, rekeying in 3308s, expires in 3952s
in  c18e28b5,    252 bytes,     3 packets,     0s ago
out c53a8dba,    252 bytes,     3 packets,     0s ago
local  10.1.0.0/24
remote 10.3.0.0/24
Test PPK PSK STS
Description
Test the site-to-site VPN with PPK authentication and PSK
Scenario
Step 1: Set the following configuration in DUT0 :
set interfaces dummy dum0 address 10.1.0.1/24
set interfaces ethernet eth1 address 80.0.0.1/24
set protocols static route 10.2.0.0/24 interface dum0
set protocols static route 10.3.0.0/24 interface dum0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk test encrypted-secret U2FsdGVkX18010NzuuRnDBYqDwoJGcGCL9LDRKS3gjk=
set vpn ipsec auth-profile AUTH-SA global-secrets ppk carol@teldat.org file 'running://ppk_carol.key'
set vpn ipsec auth-profile AUTH-SA global-secrets ppk dave@teldat.org file 'running://ppk_dave.key'
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id test
set vpn ipsec auth-profile AUTH-SA mirror-config false
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec auth-profile AUTH-SA remote ppk id '*@teldat.org'
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec logging log-types any log-level 1
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type respond
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER local-address 80.0.0.1
set vpn ipsec site-to-site peer PEER tunnel 1 local prefix 10.1.0.0/24
set vpn ipsec site-to-site peer PEER tunnel 1 local-interface dum0
Step 2: Set the following configuration in DUT1 :
set interfaces dummy dum0 address 10.2.0.1/24
set interfaces ethernet eth1 address 80.0.0.2/24
set protocols static route 10.1.0.0/24 interface dum0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk test encrypted-secret U2FsdGVkX1+t+JH4XKmsLFokK2BcwpyE2sGyW+DMRas=
set vpn ipsec auth-profile AUTH-SA global-secrets ppk carol@teldat.org file 'running://ppk_carol.key'
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id test
set vpn ipsec auth-profile AUTH-SA local ppk id carol@teldat.org
set vpn ipsec auth-profile AUTH-SA mirror-config false
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec logging log-types any log-level 1
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type initiate
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER local-address 80.0.0.2
set vpn ipsec site-to-site peer PEER remote-address 80.0.0.1
set vpn ipsec site-to-site peer PEER tunnel 1 local prefix 10.2.0.0/24
set vpn ipsec site-to-site peer PEER tunnel 1 local-interface dum0
set vpn ipsec site-to-site peer PEER tunnel 1 remote prefix 10.1.0.0/24
Step 3: Ping the IP address 80.0.0.2 from DUT1:
admin@DUT1$ ping 80.0.0.2 count 1 size 56 timeout 1Show output
PING 80.0.0.2 (80.0.0.2) 56(84) bytes of data.
64 bytes from 80.0.0.2: icmp_seq=1 ttl=64 time=0.457 ms

--- 80.0.0.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.457/0.457/0.457/0.000 ms
Step 4: Ping the IP address 80.0.0.1 from DUT0:
admin@DUT0$ ping 80.0.0.1 count 1 size 56 timeout 1Show output
PING 80.0.0.1 (80.0.0.1) 56(84) bytes of data.
64 bytes from 80.0.0.1: icmp_seq=1 ttl=64 time=0.038 ms

--- 80.0.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.038/0.038/0.038/0.000 ms
Step 5: Set the following configuration in DUT2 :
set interfaces dummy dum0 address 10.3.0.1/24
set interfaces ethernet eth1 address 80.0.0.3/24
set protocols static route 0.0.0.0/0 interface dum0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk test encrypted-secret U2FsdGVkX19Tm6DcWK7PJ337JcIpD+09zQ3lXLmuF2s=
set vpn ipsec auth-profile AUTH-SA global-secrets ppk dave@teldat.org file 'running://ppk_dave.key'
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id test
set vpn ipsec auth-profile AUTH-SA local ppk id dave@teldat.org
set vpn ipsec auth-profile AUTH-SA mirror-config false
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec logging log-types any log-level 1
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type initiate
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER local-address 80.0.0.3
set vpn ipsec site-to-site peer PEER remote-address 80.0.0.1
set vpn ipsec site-to-site peer PEER tunnel 1 local prefix 10.3.0.0/24
set vpn ipsec site-to-site peer PEER tunnel 1 local-interface dum0
set vpn ipsec site-to-site peer PEER tunnel 1 remote prefix 10.1.0.0/24
Step 6: Ping the IP address 10.1.0.1 from DUT2:
admin@DUT2$ ping 10.1.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=1.11 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 1.114/1.114/1.114/0.000 ms
Step 7: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256\/PPK.*\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*remote\s+10.2.0.*Show output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, 8e2540e7620cc7ab_i d27caf10b075e879_r*
local  'test' @ 80.0.0.1[500]
remote 'test' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 5s ago, rekeying in 23383s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 5s ago, rekeying in 3320s, expires in 3955s
in  c0d05664,      0 bytes,     0 packets
out cbb9eb88,      0 bytes,     0 packets
local  10.1.0.0/24
remote 10.2.0.0/24
vpn-peer-PEER: #2, ESTABLISHED, IKEv2, 0fdcc49ec2bc5876_i cceada45df40cf2a_r*
local  'test' @ 80.0.0.1[500]
remote 'test' @ 80.0.0.3[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 0s ago, rekeying in 19170s
peer-PEER-tunnel-1: #2, reqid 2, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 0s ago, rekeying in 3474s, expires in 3960s
in  cb366d38,     84 bytes,     1 packets,     0s ago
out ceee4ce1,     84 bytes,     1 packets,     0s ago
local  10.1.0.0/24
remote 10.3.0.0/24
Step 8: Ping the IP address 10.2.0.1 from DUT0:
admin@DUT0$ ping 10.2.0.1 local-address 10.1.0.1 count 1 size 56 timeout 1Show output
PING 10.2.0.1 (10.2.0.1) from 10.1.0.1 : 56(84) bytes of data.
64 bytes from 10.2.0.1: icmp_seq=1 ttl=64 time=0.426 ms

--- 10.2.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.426/0.426/0.426/0.000 ms
Step 9: Ping the IP address 10.1.0.1 from DUT1:
admin@DUT1$ ping 10.1.0.1 local-address 10.2.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.2.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.728 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.728/0.728/0.728/0.000 ms
Step 10: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256\/PPK.*\s+.*\s+.*\s+.*\s+.*[1-9]\d? packets.*\s+.*[1-9]\d? packets.*\s+.*\s+.*remote\s+10.2.0.*Show output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, 8e2540e7620cc7ab_i d27caf10b075e879_r*
local  'test' @ 80.0.0.1[500]
remote 'test' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 5s ago, rekeying in 23383s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 5s ago, rekeying in 3320s, expires in 3955s
in  c0d05664,    168 bytes,     2 packets,     0s ago
out cbb9eb88,    168 bytes,     2 packets,     0s ago
local  10.1.0.0/24
remote 10.2.0.0/24
vpn-peer-PEER: #2, ESTABLISHED, IKEv2, 0fdcc49ec2bc5876_i cceada45df40cf2a_r*
local  'test' @ 80.0.0.1[500]
remote 'test' @ 80.0.0.3[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 0s ago, rekeying in 19170s
peer-PEER-tunnel-1: #2, reqid 2, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 0s ago, rekeying in 3474s, expires in 3960s
in  cb366d38,     84 bytes,     1 packets,     0s ago
out ceee4ce1,     84 bytes,     1 packets,     0s ago
local  10.1.0.0/24
remote 10.3.0.0/24
Step 11: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256\/PPK\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*remote\s+10.3.0.*Show output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, 8e2540e7620cc7ab_i d27caf10b075e879_r*
local  'test' @ 80.0.0.1[500]
remote 'test' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 5s ago, rekeying in 23383s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 5s ago, rekeying in 3320s, expires in 3955s
in  c0d05664,    168 bytes,     2 packets,     0s ago
out cbb9eb88,    168 bytes,     2 packets,     0s ago
local  10.1.0.0/24
remote 10.2.0.0/24
vpn-peer-PEER: #2, ESTABLISHED, IKEv2, 0fdcc49ec2bc5876_i cceada45df40cf2a_r*
local  'test' @ 80.0.0.1[500]
remote 'test' @ 80.0.0.3[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 0s ago, rekeying in 19170s
peer-PEER-tunnel-1: #2, reqid 2, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 0s ago, rekeying in 3474s, expires in 3960s
in  cb366d38,     84 bytes,     1 packets,     0s ago
out ceee4ce1,     84 bytes,     1 packets,     0s ago
local  10.1.0.0/24
remote 10.3.0.0/24
Step 12: Ping the IP address 10.3.0.1 from DUT0:
admin@DUT0$ ping 10.3.0.1 local-address 10.1.0.1 count 1 size 56 timeout 1Show output
PING 10.3.0.1 (10.3.0.1) from 10.1.0.1 : 56(84) bytes of data.
64 bytes from 10.3.0.1: icmp_seq=1 ttl=64 time=0.342 ms

--- 10.3.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.342/0.342/0.342/0.000 ms
Step 13: Ping the IP address 10.1.0.1 from DUT2:
admin@DUT2$ ping 10.1.0.1 local-address 10.3.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.3.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.613 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.613/0.613/0.613/0.000 ms
Step 14: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256\/PPK\s+.*\s+.*\s+.*\s+.*[1-9]\d? packets.*\s+.*[1-9]\d? packets.*\s+.*\s+.*remote\s+10.3.0.*Show output
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, 8e2540e7620cc7ab_i d27caf10b075e879_r*
local  'test' @ 80.0.0.1[500]
remote 'test' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 12s ago, rekeying in 23376s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 12s ago, rekeying in 3313s, expires in 3948s
in  c0d05664,    168 bytes,     2 packets,     7s ago
out cbb9eb88,    168 bytes,     2 packets,     7s ago
local  10.1.0.0/24
remote 10.2.0.0/24
vpn-peer-PEER: #2, ESTABLISHED, IKEv2, 0fdcc49ec2bc5876_i cceada45df40cf2a_r*
local  'test' @ 80.0.0.1[500]
remote 'test' @ 80.0.0.3[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 7s ago, rekeying in 19163s
peer-PEER-tunnel-1: #2, reqid 2, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 7s ago, rekeying in 3467s, expires in 3953s
in  cb366d38,    252 bytes,     3 packets,     0s ago
out ceee4ce1,    252 bytes,     3 packets,     0s ago
local  10.1.0.0/24
remote 10.3.0.0/24
Test PPK RSA STS
Description
Test the site-to-site VPN with PPK authentication and RSA
Scenario
Step 1: Set the following configuration in DUT0 :
set interfaces dummy dum0 address 10.1.0.1/24
set interfaces ethernet eth1 address 80.0.0.1/24
set protocols static route 10.2.0.0/24 interface dum0
set protocols static route 10.3.0.0/24 interface dum0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ppk carol@teldat.org file 'running://ppk_carol.key'
set vpn ipsec auth-profile AUTH-SA global-secrets ppk dave@teldat.org file 'running://ppk_dave.key'
set vpn ipsec auth-profile AUTH-SA local ca-cert-file 'running://ca.crt'
set vpn ipsec auth-profile AUTH-SA local cert-file 'running://server.crt'
set vpn ipsec auth-profile AUTH-SA local id CN=moon.teldat.org
set vpn ipsec auth-profile AUTH-SA local key file 'running://server.priv.pem'
set vpn ipsec auth-profile AUTH-SA mirror-config false
set vpn ipsec auth-profile AUTH-SA remote ca-cert-file 'running://ca.crt'
set vpn ipsec auth-profile AUTH-SA remote ppk id '*@teldat.org'
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec logging log-types any log-level 1
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type respond
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER local-address 80.0.0.1
set vpn ipsec site-to-site peer PEER tunnel 1 local prefix 10.1.0.0/24
set vpn ipsec site-to-site peer PEER tunnel 1 local-interface dum0
Step 2: Set the following configuration in DUT1 :
set interfaces dummy dum0 address 10.2.0.1/24
set interfaces ethernet eth1 address 80.0.0.2/24
set protocols static route 10.1.0.0/24 interface dum0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ppk carol@teldat.org file 'running://ppk_carol.key'
set vpn ipsec auth-profile AUTH-SA local ca-cert-file 'running://ca.crt'
set vpn ipsec auth-profile AUTH-SA local cert-file 'running://client.crt'
set vpn ipsec auth-profile AUTH-SA local id CN=carol@teldat.org
set vpn ipsec auth-profile AUTH-SA local key file 'running://client.priv.pem'
set vpn ipsec auth-profile AUTH-SA local ppk id carol@teldat.org
set vpn ipsec auth-profile AUTH-SA mirror-config false
set vpn ipsec auth-profile AUTH-SA remote ca-cert-file 'running://ca.crt'
set vpn ipsec auth-profile AUTH-SA remote id CN=moon.teldat.org
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec logging log-types any log-level 1
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type initiate
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER local-address 80.0.0.2
set vpn ipsec site-to-site peer PEER remote-address 80.0.0.1
set vpn ipsec site-to-site peer PEER tunnel 1 local prefix 10.2.0.0/24
set vpn ipsec site-to-site peer PEER tunnel 1 local-interface dum0
set vpn ipsec site-to-site peer PEER tunnel 1 remote prefix 10.1.0.0/24
Step 3: Ping the IP address 80.0.0.2 from DUT1:
admin@DUT1$ ping 80.0.0.2 count 1 size 56 timeout 1Show output
PING 80.0.0.2 (80.0.0.2) 56(84) bytes of data.
64 bytes from 80.0.0.2: icmp_seq=1 ttl=64 time=0.038 ms

--- 80.0.0.2 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.038/0.038/0.038/0.000 ms
Step 4: Ping the IP address 80.0.0.1 from DUT0:
admin@DUT0$ ping 80.0.0.1 count 1 size 56 timeout 1Show output
PING 80.0.0.1 (80.0.0.1) 56(84) bytes of data.
64 bytes from 80.0.0.1: icmp_seq=1 ttl=64 time=0.033 ms

--- 80.0.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.033/0.033/0.033/0.000 ms
Step 5: Set the following configuration in DUT2 :
set interfaces dummy dum0 address 10.3.0.1/24
set interfaces ethernet eth1 address 80.0.0.3/24
set protocols static route 0.0.0.0/0 interface dum0
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ppk dave@teldat.org file 'running://ppk_dave.key'
set vpn ipsec auth-profile AUTH-SA local ca-cert-file 'running://ca.crt'
set vpn ipsec auth-profile AUTH-SA local cert-file 'running://client.crt'
set vpn ipsec auth-profile AUTH-SA local id CN=dave@teldat.org
set vpn ipsec auth-profile AUTH-SA local key file 'running://client.priv.pem'
set vpn ipsec auth-profile AUTH-SA local ppk id dave@teldat.org
set vpn ipsec auth-profile AUTH-SA mirror-config false
set vpn ipsec auth-profile AUTH-SA remote ca-cert-file 'running://ca.crt'
set vpn ipsec auth-profile AUTH-SA remote id CN=moon.teldat.org
set vpn ipsec esp-group CHILD-SA mode tunnel
set vpn ipsec esp-group CHILD-SA proposal 1 encryption aes256gcm128
set vpn ipsec esp-group CHILD-SA proposal 1 pfs dh-group19
set vpn ipsec ike-group IKE-SA key-exchange ikev2
set vpn ipsec ike-group IKE-SA proposal 1 dh-group 19
set vpn ipsec ike-group IKE-SA proposal 1 encryption aes256gcm128
set vpn ipsec ike-group IKE-SA proposal 1 hash sha256
set vpn ipsec logging log-types any log-level 1
set vpn ipsec site-to-site peer PEER auth-profile AUTH-SA
set vpn ipsec site-to-site peer PEER connection-type initiate
set vpn ipsec site-to-site peer PEER default-esp-group CHILD-SA
set vpn ipsec site-to-site peer PEER ike-group IKE-SA
set vpn ipsec site-to-site peer PEER local-address 80.0.0.3
set vpn ipsec site-to-site peer PEER remote-address 80.0.0.1
set vpn ipsec site-to-site peer PEER tunnel 1 local prefix 10.3.0.0/24
set vpn ipsec site-to-site peer PEER tunnel 1 local-interface dum0
set vpn ipsec site-to-site peer PEER tunnel 1 remote prefix 10.1.0.0/24
Step 6: Ping the IP address 10.1.0.1 from DUT2:
admin@DUT2$ ping 10.1.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.717 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.717/0.717/0.717/0.000 ms
Step 7: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256\/PPK.*\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*remote\s+10.2.0.*Show output
vpn-peer-PEER: #2, ESTABLISHED, IKEv2, 25c3485b8afde2d4_i e489c44babc57351_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'CN=dave@teldat.org' @ 80.0.0.3[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 1s ago, rekeying in 19942s
peer-PEER-tunnel-1: #2, reqid 2, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 1s ago, rekeying in 3262s, expires in 3959s
in  c40790a1,     84 bytes,     1 packets,     0s ago
out c7e68eda,     84 bytes,     1 packets,     0s ago
local  10.1.0.0/24
remote 10.3.0.0/24
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, 77ea7c578974a470_i f900a24b72655db5_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'CN=carol@teldat.org' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 5s ago, rekeying in 23021s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 5s ago, rekeying in 3343s, expires in 3955s
in  c27f2093,      0 bytes,     0 packets
out c31939b9,      0 bytes,     0 packets
local  10.1.0.0/24
remote 10.2.0.0/24
Step 8: Ping the IP address 10.2.0.1 from DUT0:
admin@DUT0$ ping 10.2.0.1 local-address 10.1.0.1 count 1 size 56 timeout 1Show output
PING 10.2.0.1 (10.2.0.1) from 10.1.0.1 : 56(84) bytes of data.
64 bytes from 10.2.0.1: icmp_seq=1 ttl=64 time=0.571 ms

--- 10.2.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.571/0.571/0.571/0.000 ms
Step 9: Ping the IP address 10.1.0.1 from DUT1:
admin@DUT1$ ping 10.1.0.1 local-address 10.2.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.2.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=2.22 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 2.223/2.223/2.223/0.000 ms
Step 10: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256\/PPK.*\s+.*\s+.*\s+.*\s+.*[1-9]\d? packets.*\s+.*[1-9]\d? packets.*\s+.*\s+.*remote\s+10.2.0.*Show output
vpn-peer-PEER: #2, ESTABLISHED, IKEv2, 25c3485b8afde2d4_i e489c44babc57351_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'CN=dave@teldat.org' @ 80.0.0.3[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 10s ago, rekeying in 19933s
peer-PEER-tunnel-1: #2, reqid 2, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 10s ago, rekeying in 3253s, expires in 3950s
in  c40790a1,     84 bytes,     1 packets,     9s ago
out c7e68eda,     84 bytes,     1 packets,     9s ago
local  10.1.0.0/24
remote 10.3.0.0/24
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, 77ea7c578974a470_i f900a24b72655db5_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'CN=carol@teldat.org' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 14s ago, rekeying in 23012s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 14s ago, rekeying in 3334s, expires in 3946s
in  c27f2093,    168 bytes,     2 packets,     0s ago
out c31939b9,    168 bytes,     2 packets,     0s ago
local  10.1.0.0/24
remote 10.2.0.0/24
Step 11: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256\/PPK\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*remote\s+10.3.0.*Show output
vpn-peer-PEER: #2, ESTABLISHED, IKEv2, 25c3485b8afde2d4_i e489c44babc57351_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'CN=dave@teldat.org' @ 80.0.0.3[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 10s ago, rekeying in 19933s
peer-PEER-tunnel-1: #2, reqid 2, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 10s ago, rekeying in 3253s, expires in 3950s
in  c40790a1,     84 bytes,     1 packets,     9s ago
out c7e68eda,     84 bytes,     1 packets,     9s ago
local  10.1.0.0/24
remote 10.3.0.0/24
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, 77ea7c578974a470_i f900a24b72655db5_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'CN=carol@teldat.org' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 14s ago, rekeying in 23012s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 14s ago, rekeying in 3334s, expires in 3946s
in  c27f2093,    168 bytes,     2 packets,     0s ago
out c31939b9,    168 bytes,     2 packets,     0s ago
local  10.1.0.0/24
remote 10.2.0.0/24
Step 12: Ping the IP address 10.3.0.1 from DUT0:
admin@DUT0$ ping 10.3.0.1 local-address 10.1.0.1 count 1 size 56 timeout 1Show output
PING 10.3.0.1 (10.3.0.1) from 10.1.0.1 : 56(84) bytes of data.
64 bytes from 10.3.0.1: icmp_seq=1 ttl=64 time=0.446 ms

--- 10.3.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.446/0.446/0.446/0.000 ms
Step 13: Ping the IP address 10.1.0.1 from DUT2:
admin@DUT2$ ping 10.1.0.1 local-address 10.3.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.3.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.652 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.652/0.652/0.652/0.000 ms
Step 14: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256\/PPK\s+.*\s+.*\s+.*\s+.*[1-9]\d? packets.*\s+.*[1-9]\d? packets.*\s+.*\s+.*remote\s+10.3.0.*Show output
vpn-peer-PEER: #2, ESTABLISHED, IKEv2, 25c3485b8afde2d4_i e489c44babc57351_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'CN=dave@teldat.org' @ 80.0.0.3[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 10s ago, rekeying in 19933s
peer-PEER-tunnel-1: #2, reqid 2, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 10s ago, rekeying in 3253s, expires in 3950s
in  c40790a1,    252 bytes,     3 packets,     0s ago
out c7e68eda,    252 bytes,     3 packets,     0s ago
local  10.1.0.0/24
remote 10.3.0.0/24
vpn-peer-PEER: #1, ESTABLISHED, IKEv2, 77ea7c578974a470_i f900a24b72655db5_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'CN=carol@teldat.org' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 14s ago, rekeying in 23012s
peer-PEER-tunnel-1: #1, reqid 1, INSTALLED, TUNNEL, ESP:AES_GCM_16-256
installed 14s ago, rekeying in 3334s, expires in 3946s
in  c27f2093,    168 bytes,     2 packets,     0s ago
out c31939b9,    168 bytes,     2 packets,     0s ago
local  10.1.0.0/24
remote 10.2.0.0/24
Test PPK PSK DMVPN
Description
Test the DMVPN scenario with PPK authentication and PSK
Scenario
Step 1: Set the following configuration in DUT1 :
set interfaces dummy dum0 address 10.2.0.1/24
set interfaces ethernet eth0 address 80.0.0.2/24
set interfaces tunnel tun0 address 10.0.0.2/32
set interfaces tunnel tun0 encapsulation gre
set interfaces tunnel tun0 local-address 80.0.0.2
set interfaces tunnel tun0 local-interface eth0
set interfaces tunnel tun0 mtu 1390
set interfaces tunnel tun0 nhrp holdtime 60
set interfaces tunnel tun0 nhrp ipsec IPSEC
set interfaces tunnel tun0 nhrp nhs 10.0.0.1 nbma 80.0.0.1
set protocols static route 10.1.0.0/24 next-hop 10.0.0.1
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk test encrypted-secret U2FsdGVkX18mwpqBmTx6lSpQTA77YKqkkjVK90tUAwU=
set vpn ipsec auth-profile AUTH-SA global-secrets ppk carol@teldat.org file 'running://ppk_carol.key'
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id test
set vpn ipsec auth-profile AUTH-SA local ppk id carol@teldat.org
set vpn ipsec auth-profile AUTH-SA mirror-config false
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec dmvpn-profile IPSEC auth-profile AUTH-SA
set vpn ipsec dmvpn-profile IPSEC esp-group ESP-GROUP
set vpn ipsec dmvpn-profile IPSEC ike-group IKE-GROUP
set vpn ipsec esp-group ESP-GROUP lifetime 28800
set vpn ipsec esp-group ESP-GROUP mode transport
set vpn ipsec esp-group ESP-GROUP proposal 10 encryption aes256gcm128
set vpn ipsec esp-group ESP-GROUP proposal 10 hash sha256
set vpn ipsec esp-group ESP-GROUP proposal 10 pfs dh-group19
set vpn ipsec ike-group IKE-GROUP key-exchange ikev2
set vpn ipsec ike-group IKE-GROUP lifetime 86400
set vpn ipsec ike-group IKE-GROUP proposal 10 dh-group 19
set vpn ipsec ike-group IKE-GROUP proposal 10 encryption aes256gcm128
set vpn ipsec ike-group IKE-GROUP proposal 10 hash sha256
set vpn ipsec logging log-types any log-level 1
Step 2: Set the following configuration in DUT0 :
set interfaces dummy dum0 address 10.1.0.1/24
set interfaces ethernet eth0 address 80.0.0.1/24
set interfaces tunnel tun0 address 10.0.0.1/32
set interfaces tunnel tun0 encapsulation gre
set interfaces tunnel tun0 local-address 80.0.0.1
set interfaces tunnel tun0 local-interface eth0
set interfaces tunnel tun0 mtu 1390
set interfaces tunnel tun0 nhrp holdtime 60
set interfaces tunnel tun0 nhrp ipsec IPSEC
set interfaces tunnel tun0 nhrp transport-nat-support
set protocols static route 10.2.0.0/24 next-hop 10.0.0.2
set protocols static route 10.3.0.0/24 next-hop 10.0.0.3
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk test encrypted-secret U2FsdGVkX18dSf/swCd+Zp8XX7JXAwoCOstK+yfq3YE=
set vpn ipsec auth-profile AUTH-SA global-secrets ppk carol@teldat.org file 'running://ppk_carol.key'
set vpn ipsec auth-profile AUTH-SA global-secrets ppk dave@teldat.org file 'running://ppk_dave.key'
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id test
set vpn ipsec auth-profile AUTH-SA mirror-config false
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec auth-profile AUTH-SA remote ppk id '*@teldat.org'
set vpn ipsec dmvpn-profile IPSEC auth-profile AUTH-SA
set vpn ipsec dmvpn-profile IPSEC esp-group ESP-GROUP
set vpn ipsec dmvpn-profile IPSEC ike-group IKE-GROUP
set vpn ipsec esp-group ESP-GROUP lifetime 28800
set vpn ipsec esp-group ESP-GROUP mode transport
set vpn ipsec esp-group ESP-GROUP proposal 10 encryption aes256gcm128
set vpn ipsec esp-group ESP-GROUP proposal 10 hash sha256
set vpn ipsec esp-group ESP-GROUP proposal 10 pfs dh-group19
set vpn ipsec ike-group IKE-GROUP key-exchange ikev2
set vpn ipsec ike-group IKE-GROUP lifetime 86400
set vpn ipsec ike-group IKE-GROUP proposal 10 dh-group 19
set vpn ipsec ike-group IKE-GROUP proposal 10 encryption aes256gcm128
set vpn ipsec ike-group IKE-GROUP proposal 10 hash sha256
set vpn ipsec logging log-types any log-level 1
Step 3: Ping the IP address 10.1.0.1 from DUT1:
admin@DUT1$ ping 10.1.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.895 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.895/0.895/0.895/0.000 ms
Step 4: Ping the IP address 10.2.0.1 from DUT0:
admin@DUT0$ ping 10.2.0.1 count 1 size 56 timeout 1Show output
PING 10.2.0.1 (10.2.0.1) 56(84) bytes of data.
64 bytes from 10.2.0.1: icmp_seq=1 ttl=64 time=0.469 ms

--- 10.2.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.469/0.469/0.469/0.000 ms
Step 5: Set the following configuration in DUT2 :
set interfaces dummy dum0 address 10.3.0.1/24
set interfaces ethernet eth0 address 80.0.0.3/24
set interfaces tunnel tun0 address 10.0.0.3/32
set interfaces tunnel tun0 encapsulation gre
set interfaces tunnel tun0 local-address 80.0.0.3
set interfaces tunnel tun0 local-interface eth0
set interfaces tunnel tun0 mtu 1390
set interfaces tunnel tun0 nhrp holdtime 60
set interfaces tunnel tun0 nhrp ipsec IPSEC
set interfaces tunnel tun0 nhrp nhs 10.0.0.1 nbma 80.0.0.1
set protocols static route 10.1.0.0/24 next-hop 10.0.0.1
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ike-psk test encrypted-secret U2FsdGVkX19qWdmTKvR78f1mWBxy8O6gDoLIGBOCx4o=
set vpn ipsec auth-profile AUTH-SA global-secrets ppk carol@teldat.org file 'running://ppk_carol.key'
set vpn ipsec auth-profile AUTH-SA local auth ike-psk id test
set vpn ipsec auth-profile AUTH-SA local ppk id carol@teldat.org
set vpn ipsec auth-profile AUTH-SA mirror-config false
set vpn ipsec auth-profile AUTH-SA remote auth ike-psk id %any
set vpn ipsec dmvpn-profile IPSEC auth-profile AUTH-SA
set vpn ipsec dmvpn-profile IPSEC esp-group ESP-GROUP
set vpn ipsec dmvpn-profile IPSEC ike-group IKE-GROUP
set vpn ipsec esp-group ESP-GROUP lifetime 28800
set vpn ipsec esp-group ESP-GROUP mode transport
set vpn ipsec esp-group ESP-GROUP proposal 10 encryption aes256gcm128
set vpn ipsec esp-group ESP-GROUP proposal 10 hash sha256
set vpn ipsec esp-group ESP-GROUP proposal 10 pfs dh-group19
set vpn ipsec ike-group IKE-GROUP key-exchange ikev2
set vpn ipsec ike-group IKE-GROUP lifetime 86400
set vpn ipsec ike-group IKE-GROUP proposal 10 dh-group 19
set vpn ipsec ike-group IKE-GROUP proposal 10 encryption aes256gcm128
set vpn ipsec ike-group IKE-GROUP proposal 10 hash sha256
set vpn ipsec logging log-types any log-level 1
Step 6: Ping the IP address 10.1.0.1 from DUT2:
admin@DUT2$ ping 10.1.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.592 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.592/0.592/0.592/0.000 ms
Step 7: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256\/PPK.*\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*remote\s+80.0.0.*Show output
IPSEC: #1, ESTABLISHED, IKEv2, efe2a5da67ebac52_i 2a339d4dba745189_r*
local  'test' @ 80.0.0.1[500]
remote 'test' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 12s ago, rekeying in 77696s
IPSEC: #1, reqid 1, INSTALLED, TRANSPORT, ESP:AES_GCM_16-256
installed 12s ago, rekeying in 14534s, expires in 28788s
in  c0ac7cba,    368 bytes,     4 packets,    11s ago
out c3110610,    292 bytes,     3 packets,    11s ago
local  80.0.0.1/32[gre]
remote 80.0.0.2/32[gre]
IPSEC: #2, ESTABLISHED, IKEv2, e09a981523b30e35_i cb96360139f0fd08_r*
local  'test' @ 80.0.0.1[500]
remote 'test' @ 80.0.0.3[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 0s ago, rekeying in 45327s
IPSEC: #2, reqid 2, INSTALLED, TRANSPORT, ESP:AES_GCM_16-256
installed 0s ago, rekeying in 15231s, expires in 28800s
in  c270c3b4,    184 bytes,     2 packets,     1s ago
out c226adbc,    204 bytes,     2 packets,     1s ago
local  80.0.0.1/32[gre]
remote 80.0.0.3/32[gre]
Step 8: Ping the IP address 10.2.0.1 from DUT0:
admin@DUT0$ ping 10.2.0.1 local-address 10.1.0.1 count 1 size 56 timeout 1Show output
PING 10.2.0.1 (10.2.0.1) from 10.1.0.1 : 56(84) bytes of data.
64 bytes from 10.2.0.1: icmp_seq=1 ttl=64 time=0.351 ms

--- 10.2.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.351/0.351/0.351/0.000 ms
Step 9: Ping the IP address 10.1.0.1 from DUT1:
admin@DUT1$ ping 10.1.0.1 local-address 10.2.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.2.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.819 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.819/0.819/0.819/0.000 ms
Step 10: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256\/PPK.*\s+.*\s+.*\s+.*\s+.*[1-9]\d? packets.*\s+.*[1-9]\d? packets.*\s+.*\s+.*remote\s+80.0.0\.2Show output
IPSEC: #1, ESTABLISHED, IKEv2, efe2a5da67ebac52_i 2a339d4dba745189_r*
local  'test' @ 80.0.0.1[500]
remote 'test' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 12s ago, rekeying in 77696s
IPSEC: #1, reqid 1, INSTALLED, TRANSPORT, ESP:AES_GCM_16-256
installed 12s ago, rekeying in 14534s, expires in 28788s
in  c0ac7cba,    544 bytes,     6 packets,     0s ago
out c3110610,    468 bytes,     5 packets,     0s ago
local  80.0.0.1/32[gre]
remote 80.0.0.2/32[gre]
IPSEC: #2, ESTABLISHED, IKEv2, e09a981523b30e35_i cb96360139f0fd08_r*
local  'test' @ 80.0.0.1[500]
remote 'test' @ 80.0.0.3[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 0s ago, rekeying in 45327s
IPSEC: #2, reqid 2, INSTALLED, TRANSPORT, ESP:AES_GCM_16-256
installed 0s ago, rekeying in 15231s, expires in 28800s
in  c270c3b4,    184 bytes,     2 packets,     1s ago
out c226adbc,    204 bytes,     2 packets,     1s ago
local  80.0.0.1/32[gre]
remote 80.0.0.3/32[gre]
Step 11: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256\/PPK.*\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*remote\s+80.0.0.*Show output
IPSEC: #1, ESTABLISHED, IKEv2, efe2a5da67ebac52_i 2a339d4dba745189_r*
local  'test' @ 80.0.0.1[500]
remote 'test' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 13s ago, rekeying in 77695s
IPSEC: #1, reqid 1, INSTALLED, TRANSPORT, ESP:AES_GCM_16-256
installed 13s ago, rekeying in 14533s, expires in 28787s
in  c0ac7cba,    544 bytes,     6 packets,     1s ago
out c3110610,    468 bytes,     5 packets,     1s ago
local  80.0.0.1/32[gre]
remote 80.0.0.2/32[gre]
IPSEC: #2, ESTABLISHED, IKEv2, e09a981523b30e35_i cb96360139f0fd08_r*
local  'test' @ 80.0.0.1[500]
remote 'test' @ 80.0.0.3[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 1s ago, rekeying in 45326s
IPSEC: #2, reqid 2, INSTALLED, TRANSPORT, ESP:AES_GCM_16-256
installed 1s ago, rekeying in 15230s, expires in 28799s
in  c270c3b4,    184 bytes,     2 packets,     2s ago
out c226adbc,    204 bytes,     2 packets,     2s ago
local  80.0.0.1/32[gre]
remote 80.0.0.3/32[gre]
Step 12: Ping the IP address 10.3.0.1 from DUT0:
admin@DUT0$ ping 10.3.0.1 local-address 10.1.0.1 count 1 size 56 timeout 1Show output
PING 10.3.0.1 (10.3.0.1) from 10.1.0.1 : 56(84) bytes of data.
64 bytes from 10.3.0.1: icmp_seq=1 ttl=64 time=0.402 ms

--- 10.3.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.402/0.402/0.402/0.000 ms
Step 13: Ping the IP address 10.1.0.1 from DUT2:
admin@DUT2$ ping 10.1.0.1 local-address 10.3.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.3.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.665 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.665/0.665/0.665/0.000 ms
Step 14: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256\/PPK.*\s+.*\s+.*\s+.*\s+.*[1-9]\d? packets.*\s+.*[1-9]\d? packets.*\s+.*\s+.*remote\s+80.0.0\.3.*Show output
IPSEC: #1, ESTABLISHED, IKEv2, efe2a5da67ebac52_i 2a339d4dba745189_r*
local  'test' @ 80.0.0.1[500]
remote 'test' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 13s ago, rekeying in 77695s
IPSEC: #1, reqid 1, INSTALLED, TRANSPORT, ESP:AES_GCM_16-256
installed 13s ago, rekeying in 14533s, expires in 28787s
in  c0ac7cba,    544 bytes,     6 packets,     1s ago
out c3110610,    468 bytes,     5 packets,     1s ago
local  80.0.0.1/32[gre]
remote 80.0.0.2/32[gre]
IPSEC: #2, ESTABLISHED, IKEv2, e09a981523b30e35_i cb96360139f0fd08_r*
local  'test' @ 80.0.0.1[500]
remote 'test' @ 80.0.0.3[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 1s ago, rekeying in 45326s
IPSEC: #2, reqid 2, INSTALLED, TRANSPORT, ESP:AES_GCM_16-256
installed 1s ago, rekeying in 15230s, expires in 28799s
in  c270c3b4,    360 bytes,     4 packets,     0s ago
out c226adbc,    380 bytes,     4 packets,     0s ago
local  80.0.0.1/32[gre]
remote 80.0.0.3/32[gre]
Step 15: Run the command protocols ip show nhrp on DUT0 and expect the following output:
Show output
Iface      Type     Protocol         NBMA             Claimed NBMA     Expires(s)   Flags  Identity
tun0       local    10.0.0.1         80.0.0.1         80.0.0.1         -                   -
tun0       dynamic  10.0.0.3         80.0.0.3         80.0.0.3         59            TA    test
tun0       dynamic  10.0.0.2         80.0.0.2         80.0.0.2         48            T     test
Test PPK RSA DMVPN
Description
Test the DMVPN scenario with PPK authentication and RSA, with same ppk on both remotes.
Scenario
Step 1: Set the following configuration in DUT1 :
set interfaces dummy dum0 address 10.2.0.1/24
set interfaces ethernet eth0 address 80.0.0.2/24
set interfaces tunnel tun0 address 10.0.0.2/32
set interfaces tunnel tun0 encapsulation gre
set interfaces tunnel tun0 local-address 80.0.0.2
set interfaces tunnel tun0 local-interface eth0
set interfaces tunnel tun0 mtu 1390
set interfaces tunnel tun0 nhrp holdtime 60
set interfaces tunnel tun0 nhrp ipsec IPSEC
set interfaces tunnel tun0 nhrp nhs 10.0.0.1 nbma 80.0.0.1
set protocols static route 10.1.0.0/24 next-hop 10.0.0.1
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ppk carol@teldat.org file 'running://ppk_carol.key'
set vpn ipsec auth-profile AUTH-SA local ca-cert-file 'running://ca.crt'
set vpn ipsec auth-profile AUTH-SA local cert-file 'running://client.crt'
set vpn ipsec auth-profile AUTH-SA local id CN=carol@teldat.org
set vpn ipsec auth-profile AUTH-SA local key file 'running://client.priv.pem'
set vpn ipsec auth-profile AUTH-SA local ppk id carol@teldat.org
set vpn ipsec auth-profile AUTH-SA mirror-config false
set vpn ipsec auth-profile AUTH-SA remote ca-cert-file 'running://ca.crt'
set vpn ipsec auth-profile AUTH-SA remote id CN=moon.teldat.org
set vpn ipsec dmvpn-profile IPSEC auth-profile AUTH-SA
set vpn ipsec dmvpn-profile IPSEC esp-group ESP-GROUP
set vpn ipsec dmvpn-profile IPSEC ike-group IKE-GROUP
set vpn ipsec esp-group ESP-GROUP lifetime 28800
set vpn ipsec esp-group ESP-GROUP mode transport
set vpn ipsec esp-group ESP-GROUP proposal 10 encryption aes256gcm128
set vpn ipsec esp-group ESP-GROUP proposal 10 hash sha256
set vpn ipsec esp-group ESP-GROUP proposal 10 pfs dh-group19
set vpn ipsec ike-group IKE-GROUP key-exchange ikev2
set vpn ipsec ike-group IKE-GROUP lifetime 86400
set vpn ipsec ike-group IKE-GROUP proposal 10 dh-group 19
set vpn ipsec ike-group IKE-GROUP proposal 10 encryption aes256gcm128
set vpn ipsec ike-group IKE-GROUP proposal 10 hash sha256
set vpn ipsec logging log-types any log-level 1
Step 2: Set the following configuration in DUT0 :
set interfaces dummy dum0 address 10.1.0.1/24
set interfaces ethernet eth0 address 80.0.0.1/24
set interfaces tunnel tun0 address 10.0.0.1/32
set interfaces tunnel tun0 encapsulation gre
set interfaces tunnel tun0 local-address 80.0.0.1
set interfaces tunnel tun0 local-interface eth0
set interfaces tunnel tun0 mtu 1390
set interfaces tunnel tun0 nhrp holdtime 60
set interfaces tunnel tun0 nhrp ipsec IPSEC
set interfaces tunnel tun0 nhrp transport-nat-support
set protocols static route 10.2.0.0/24 next-hop 10.0.0.2
set protocols static route 10.3.0.0/24 next-hop 10.0.0.3
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ppk carol@teldat.org file 'running://ppk_carol.key'
set vpn ipsec auth-profile AUTH-SA global-secrets ppk dave@teldat.org file 'running://ppk_dave.key'
set vpn ipsec auth-profile AUTH-SA local ca-cert-file 'running://ca.crt'
set vpn ipsec auth-profile AUTH-SA local cert-file 'running://server.crt'
set vpn ipsec auth-profile AUTH-SA local id CN=moon.teldat.org
set vpn ipsec auth-profile AUTH-SA local key file 'running://server.priv.pem'
set vpn ipsec auth-profile AUTH-SA mirror-config false
set vpn ipsec auth-profile AUTH-SA remote ca-cert-file 'running://ca.crt'
set vpn ipsec auth-profile AUTH-SA remote ppk id '*@teldat.org'
set vpn ipsec dmvpn-profile IPSEC auth-profile AUTH-SA
set vpn ipsec dmvpn-profile IPSEC esp-group ESP-GROUP
set vpn ipsec dmvpn-profile IPSEC ike-group IKE-GROUP
set vpn ipsec esp-group ESP-GROUP lifetime 28800
set vpn ipsec esp-group ESP-GROUP mode transport
set vpn ipsec esp-group ESP-GROUP proposal 10 encryption aes256gcm128
set vpn ipsec esp-group ESP-GROUP proposal 10 hash sha256
set vpn ipsec esp-group ESP-GROUP proposal 10 pfs dh-group19
set vpn ipsec ike-group IKE-GROUP key-exchange ikev2
set vpn ipsec ike-group IKE-GROUP lifetime 86400
set vpn ipsec ike-group IKE-GROUP proposal 10 dh-group 19
set vpn ipsec ike-group IKE-GROUP proposal 10 encryption aes256gcm128
set vpn ipsec ike-group IKE-GROUP proposal 10 hash sha256
set vpn ipsec logging log-types any log-level 1
Step 3: Ping the IP address 10.1.0.1 from DUT1:
admin@DUT1$ ping 10.1.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.397 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.397/0.397/0.397/0.000 ms
Step 4: Ping the IP address 10.2.0.1 from DUT0:
admin@DUT0$ ping 10.2.0.1 count 1 size 56 timeout 1Show output
PING 10.2.0.1 (10.2.0.1) 56(84) bytes of data.
64 bytes from 10.2.0.1: icmp_seq=1 ttl=64 time=0.646 ms

--- 10.2.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.646/0.646/0.646/0.000 ms
Step 5: Set the following configuration in DUT2 :
set interfaces dummy dum0 address 10.3.0.1/24
set interfaces ethernet eth0 address 80.0.0.3/24
set interfaces tunnel tun0 address 10.0.0.3/32
set interfaces tunnel tun0 encapsulation gre
set interfaces tunnel tun0 local-address 80.0.0.3
set interfaces tunnel tun0 local-interface eth0
set interfaces tunnel tun0 mtu 1390
set interfaces tunnel tun0 nhrp holdtime 60
set interfaces tunnel tun0 nhrp ipsec IPSEC
set interfaces tunnel tun0 nhrp nhs 10.0.0.1 nbma 80.0.0.1
set protocols static route 10.1.0.0/24 next-hop 10.0.0.1
set system login user admin authentication encrypted-password '$6$GSjsCj8gHLv$/VcqU6FLi6CT2Oxn0MJQ2C2tqnRDrYKNF8HIYWJp68nvXvPdFccDsT04.WtigUONbKYrgKg8d6rEs8PjljMkH0'
set vpn ipsec auth-profile AUTH-SA global-secrets ppk carol@teldat.org file 'running://ppk_carol.key'
set vpn ipsec auth-profile AUTH-SA local ca-cert-file 'running://ca.crt'
set vpn ipsec auth-profile AUTH-SA local cert-file 'running://client.crt'
set vpn ipsec auth-profile AUTH-SA local id CN=dave@teldat.org
set vpn ipsec auth-profile AUTH-SA local key file 'running://client.priv.pem'
set vpn ipsec auth-profile AUTH-SA local ppk id carol@teldat.org
set vpn ipsec auth-profile AUTH-SA mirror-config false
set vpn ipsec auth-profile AUTH-SA remote ca-cert-file 'running://ca.crt'
set vpn ipsec auth-profile AUTH-SA remote id CN=moon.teldat.org
set vpn ipsec dmvpn-profile IPSEC auth-profile AUTH-SA
set vpn ipsec dmvpn-profile IPSEC esp-group ESP-GROUP
set vpn ipsec dmvpn-profile IPSEC ike-group IKE-GROUP
set vpn ipsec esp-group ESP-GROUP lifetime 28800
set vpn ipsec esp-group ESP-GROUP mode transport
set vpn ipsec esp-group ESP-GROUP proposal 10 encryption aes256gcm128
set vpn ipsec esp-group ESP-GROUP proposal 10 hash sha256
set vpn ipsec esp-group ESP-GROUP proposal 10 pfs dh-group19
set vpn ipsec ike-group IKE-GROUP key-exchange ikev2
set vpn ipsec ike-group IKE-GROUP lifetime 86400
set vpn ipsec ike-group IKE-GROUP proposal 10 dh-group 19
set vpn ipsec ike-group IKE-GROUP proposal 10 encryption aes256gcm128
set vpn ipsec ike-group IKE-GROUP proposal 10 hash sha256
set vpn ipsec logging log-types any log-level 1
Step 6: Ping the IP address 10.1.0.1 from DUT2:
admin@DUT2$ ping 10.1.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.379 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.379/0.379/0.379/0.000 ms
Warning
“Certificates must include the IP address in the SAN field, otherwise the connection will fail.”
Step 7: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256\/PPK.*\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*remote\s+80.0.0.*Show output
IPSEC: #2, ESTABLISHED, IKEv2, fa961e4609d698a1_i 88fcf7ae83a3eac3_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'CN=dave@teldat.org' @ 80.0.0.3[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 1s ago, rekeying in 58003s
IPSEC: #2, reqid 2, INSTALLED, TRANSPORT, ESP:AES_GCM_16-256
installed 1s ago, rekeying in 18553s, expires in 28799s
in  c18bd659,    184 bytes,     2 packets,     1s ago
out cf4a79a6,    204 bytes,     2 packets,     1s ago
local  80.0.0.1/32[gre]
remote 80.0.0.3/32[gre]
IPSEC: #1, ESTABLISHED, IKEv2, 4a543ef20fdc2095_i e93960ea16f9f97c_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'CN=carol@teldat.org' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 11s ago, rekeying in 61053s
IPSEC: #1, reqid 1, INSTALLED, TRANSPORT, ESP:AES_GCM_16-256
installed 11s ago, rekeying in 14866s, expires in 28789s
in  c69ae994,    272 bytes,     3 packets,    12s ago
out c7feb561,    292 bytes,     3 packets,    12s ago
local  80.0.0.1/32[gre]
remote 80.0.0.2/32[gre]
Step 8: Ping the IP address 10.2.0.1 from DUT0:
admin@DUT0$ ping 10.2.0.1 local-address 10.1.0.1 count 1 size 56 timeout 1Show output
PING 10.2.0.1 (10.2.0.1) from 10.1.0.1 : 56(84) bytes of data.
64 bytes from 10.2.0.1: icmp_seq=1 ttl=64 time=0.933 ms

--- 10.2.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.933/0.933/0.933/0.000 ms
Step 9: Ping the IP address 10.1.0.1 from DUT1:
admin@DUT1$ ping 10.1.0.1 local-address 10.2.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.2.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.744 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.744/0.744/0.744/0.000 ms
Step 10: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256\/PPK.*\s+.*\s+.*\s+.*\s+.*[1-9]\d? packets.*\s+.*[1-9]\d? packets.*\s+.*\s+.*remote\s+80.0.0\.2Show output
IPSEC: #2, ESTABLISHED, IKEv2, fa961e4609d698a1_i 88fcf7ae83a3eac3_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'CN=dave@teldat.org' @ 80.0.0.3[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 1s ago, rekeying in 58003s
IPSEC: #2, reqid 2, INSTALLED, TRANSPORT, ESP:AES_GCM_16-256
installed 1s ago, rekeying in 18553s, expires in 28799s
in  c18bd659,    184 bytes,     2 packets,     1s ago
out cf4a79a6,    204 bytes,     2 packets,     1s ago
local  80.0.0.1/32[gre]
remote 80.0.0.3/32[gre]
IPSEC: #1, ESTABLISHED, IKEv2, 4a543ef20fdc2095_i e93960ea16f9f97c_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'CN=carol@teldat.org' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 11s ago, rekeying in 61053s
IPSEC: #1, reqid 1, INSTALLED, TRANSPORT, ESP:AES_GCM_16-256
installed 11s ago, rekeying in 14866s, expires in 28789s
in  c69ae994,    448 bytes,     5 packets,     0s ago
out c7feb561,    468 bytes,     5 packets,     0s ago
local  80.0.0.1/32[gre]
remote 80.0.0.2/32[gre]
Step 11: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256\/PPK.*\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*\s+.*remote\s+80.0.0.*Show output
IPSEC: #2, ESTABLISHED, IKEv2, fa961e4609d698a1_i 88fcf7ae83a3eac3_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'CN=dave@teldat.org' @ 80.0.0.3[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 1s ago, rekeying in 58003s
IPSEC: #2, reqid 2, INSTALLED, TRANSPORT, ESP:AES_GCM_16-256
installed 1s ago, rekeying in 18553s, expires in 28799s
in  c18bd659,    184 bytes,     2 packets,     1s ago
out cf4a79a6,    204 bytes,     2 packets,     1s ago
local  80.0.0.1/32[gre]
remote 80.0.0.3/32[gre]
IPSEC: #1, ESTABLISHED, IKEv2, 4a543ef20fdc2095_i e93960ea16f9f97c_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'CN=carol@teldat.org' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 11s ago, rekeying in 61053s
IPSEC: #1, reqid 1, INSTALLED, TRANSPORT, ESP:AES_GCM_16-256
installed 11s ago, rekeying in 14866s, expires in 28789s
in  c69ae994,    448 bytes,     5 packets,     0s ago
out c7feb561,    468 bytes,     5 packets,     0s ago
local  80.0.0.1/32[gre]
remote 80.0.0.2/32[gre]
Step 12: Ping the IP address 10.3.0.1 from DUT0:
admin@DUT0$ ping 10.3.0.1 local-address 10.1.0.1 count 1 size 56 timeout 1Show output
PING 10.3.0.1 (10.3.0.1) from 10.1.0.1 : 56(84) bytes of data.
64 bytes from 10.3.0.1: icmp_seq=1 ttl=64 time=0.967 ms

--- 10.3.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.967/0.967/0.967/0.000 ms
Step 13: Ping the IP address 10.1.0.1 from DUT2:
admin@DUT2$ ping 10.1.0.1 local-address 10.3.0.1 count 1 size 56 timeout 1Show output
PING 10.1.0.1 (10.1.0.1) from 10.3.0.1 : 56(84) bytes of data.
64 bytes from 10.1.0.1: icmp_seq=1 ttl=64 time=0.601 ms

--- 10.1.0.1 ping statistics ---
1 packets transmitted, 1 received, 0% packet loss, time 0ms
rtt min/avg/max/mdev = 0.601/0.601/0.601/0.000 ms
Step 14: Run the command vpn ipsec show sa on DUT0 and check whether the output matches the following regular expressions:
(?m)\s+.*AES_GCM_16-256\/PRF_HMAC_SHA2_256\/ECP_256\/PPK.*\s+.*\s+.*\s+.*\s+.*[1-9]\d? packets.*\s+.*[1-9]\d? packets.*\s+.*\s+.*remote\s+80.0.0\.3.*Show output
IPSEC: #2, ESTABLISHED, IKEv2, fa961e4609d698a1_i 88fcf7ae83a3eac3_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'CN=dave@teldat.org' @ 80.0.0.3[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 2s ago, rekeying in 58002s
IPSEC: #2, reqid 2, INSTALLED, TRANSPORT, ESP:AES_GCM_16-256
installed 2s ago, rekeying in 18552s, expires in 28798s
in  c18bd659,    360 bytes,     4 packets,     0s ago
out cf4a79a6,    380 bytes,     4 packets,     0s ago
local  80.0.0.1/32[gre]
remote 80.0.0.3/32[gre]
IPSEC: #1, ESTABLISHED, IKEv2, 4a543ef20fdc2095_i e93960ea16f9f97c_r*
local  'CN=moon.teldat.org' @ 80.0.0.1[500]
remote 'CN=carol@teldat.org' @ 80.0.0.2[500]
AES_GCM_16-256/PRF_HMAC_SHA2_256/ECP_256/PPK
established 12s ago, rekeying in 61052s
IPSEC: #1, reqid 1, INSTALLED, TRANSPORT, ESP:AES_GCM_16-256
installed 12s ago, rekeying in 14865s, expires in 28788s
in  c69ae994,    448 bytes,     5 packets,     1s ago
out c7feb561,    468 bytes,     5 packets,     1s ago
local  80.0.0.1/32[gre]
remote 80.0.0.2/32[gre]